The Preparedness Gap: From Capability to Coordination
Europe’s Preparedness Era
Europe’s approach to security has undergone a profound transformation. For decades, policy debates concentrated on identifying threats, strengthening protective measures and developing the capabilities needed to respond to crises. While these priorities remain essential, the focus has gradually shifted from resilience towards preparedness. The question is no longer simply whether Europe possesses sufficient capabilities, but whether it is prepared to organise and mobilise them effectively when they are needed most.
This evolution is reflected in recent European initiatives, including the Critical Entities Resilience (CER) Directive, the NIS2 Directive and, more recently, the Preparedness Union Strategy. Together, they signal a broader understanding of resilience, one that extends beyond emergency response to encompass anticipation, coordination and the ability of society as a whole to withstand, manage and recover from disruption.
Preparedness is therefore no longer solely the responsibility of governments or emergency services. It requires a whole-of-society approach in which public authorities, Critical Infrastructure operators, emergency responders, businesses and relevant regulated actors each contribute to a shared resilience architecture.
Yet despite this evolution, an important challenge remains largely overlooked.
Across Europe, many of the capabilities that would prove essential during a crisis already exist. Public authorities, emergency services, Critical Infrastructure operators, regulated private security providers, specialised technology operators and other essential actors protect critical infrastructure, monitor sensitive facilities, respond to alarms, secure transport networks, support business continuity and provide situational awareness around the clock.
However, these capabilities are still too often brought together only after a crisis has begun, in the absence of agreed governance arrangements, communication protocols, operational procedures and established coordination mechanisms.
This article argues that Europe faces not only capability gaps, but also what I describe as the Preparedness Gap: the gap between the capabilities and experience available within society and those effectively recognised, integrated and institutionalised as part of preparedness before a crisis occurs.
Closing this gap requires more than additional investment or new technologies. It requires a shift in mindset: from viewing resilience as the accumulation of capabilities to understanding it as the organisation of capabilities.
Private security offers a compelling illustration of this broader challenge. With approximately two million licensed professionals operating across Europe, the sector contributes daily to the protection of airports, ports, energy facilities, hospitals, public institutions, transport networks and countless other critical assets. Yet despite this operational presence, the sector’s capabilities, expertise and operational resources are frequently incorporated into preparedness arrangements only when emergencies are already unfolding. This is not simply a challenge for one sector. It reflects a broader governance challenge that is relevant to every organisation responsible for preparedness and the protection of society.
Preparedness therefore raises a broader question than capability development alone:
How can existing capabilities become an integral part of resilience before, not during, the next crisis?
The Preparedness Gap
Public policy frequently refers to capability gaps, skills shortages or technological deficits. These concepts assume that resilience depends primarily on acquiring what is missing. While this remains true in some areas, it does not fully explain why well-equipped societies continue to encounter coordination challenges during major emergencies.
Increasingly, Europe’s preparedness challenge lies elsewhere. In many cases, the necessary capabilities already exist, but they remain insufficiently recognised, connected and embedded within preparedness planning.
I therefore propose a complementary concept: the Preparedness Gap.
The Preparedness Gap is the difference between the capabilities and experience available within society and those effectively recognised and fully integrated in governance, procedures and operational planning, as part of preparedness before a crisis occurs.
In practical terms, preparedness means that roles and responsibilities, communication protocols, standard operating procedures, information-sharing mechanisms, legal authorities and decision-making processes have already been agreed, tested and exercised before an emergency arises. It also means that procurement models are designed for long-term resilience, not short-term cost efficiency. And finally, it makes sure that valuable operational experience gained during previous crises is translated into permanent institutional practice.
In short, preparedness is about ensuring that every relevant capability, and every relevant lesson, has already been recognised, connected and embedded before the first alarm is raised. This saves precious time and energy in crises, during which these resources are most scarce.
Why the Preparedness Gap Persists
The Preparedness Gap rarely results from a single policy failure. Rather, it emerges from the gradual accumulation of decisions taken across different policy domains, often with legitimate but disconnected objectives. Legal frameworks, procurement models, operational planning and institutional cultures have evolved in parallel rather than together, creating preparedness systems in which existing capabilities are not always fully connected.
Closing the Preparedness Gap therefore requires more than additional resources. It requires preparedness to be understood as a question of governance.
Four dimensions deserve particular attention.
Recognition
Preparedness begins by recognising which capabilities already exist within society.
Many preparedness frameworks understandably focus on public institutions and emergency responders. Yet resilience increasingly depends on a much broader ecosystem of stakeholders that contribute to the protection of Critical Infrastructure every day. Recognition does not imply transferring public responsibilities or blurring lines of authority. Rather, it means acknowledging operational realities and understanding how existing capabilities can contribute more effectively before, during and after crises.
Recognition is therefore the first step towards integration. Capabilities cannot become part of preparedness if they are absent from preparedness planning.
Integration 
Recognition alone is not enough. Capabilities become operationally meaningful only when they are translated into preparedness.
That requires more than acknowledging their existence. It means embedding them in contingency planning, governance arrangements, communication protocols, information-sharing mechanisms, joint exercises and clearly defined responsibilities before a crisis occurs.
In practice, however, cooperation often develops only out of operational necessity. Public authorities, Critical Infrastructure operators and private actors establish pragmatic, ad hoc working relationships because circumstances leave them little alternative. These improvised arrangements frequently demonstrate remarkable professionalism and commitment. They also consume valuable time and energy at precisely the moment when both are most limited.
The more fundamental challenge emerges after the crisis.
Once normality returns, temporary cooperation too often disappears with it. Operational experience is acknowledged, reports are produced and participants are thanked for their commitment. Yet valuable lessons are not always translated into revised governance, updated contingency plans, regular joint exercises or permanent cooperation mechanisms.
As a result, each new crisis risks beginning with many of the same conversations, uncertainties and organisational barriers as the previous one.
The issue is not whether societies learn from crises. It is whether institutions learn quickly enough to transform operational experience into permanent preparedness.
Preparedness should ensure that cooperation no longer depends on operational necessity alone, but becomes a permanent feature of resilience.
Governance
Preparedness also depends on clarity.
• Who has the authority to act?
• Who shares information, with whom, and under what conditions?
• Who makes operational decisions?
• Who assumes responsibility?
• How are roles and responsibilities coordinated across organisations?
These questions often prove more complex than the technologies themselves. Without clearly defined governance arrangements, even highly capable organisations struggle to work together efficiently under pressure.
Governance is therefore not an administrative layer added to preparedness. It is the mechanism through which individual capabilities become collective resilience.
Sustainability
Preparedness cannot be separated from the long-term sustainability of essential capabilities.
Resilience depends on organisations being able to recruit, train and retain qualified professionals, invest in innovation and maintain operational readiness over time.
Procurement strategies that prioritise lowest price at the expense of quality may appear economically efficient in the short term, yet they can gradually erode the capabilities upon which preparedness ultimately relies. Workforce resilience, professional standards and sustained investment are therefore not simply economic concerns; they are integral components of preparedness itself.
Three Symptoms of the Preparedness Gap
The Preparedness Gap is rarely visible during routine operations. It becomes apparent when crises expose the disconnect between existing capabilities and the governance arrangements needed to mobilise them effectively.
The following examples come from different operational domains. They involve different technologies, legal frameworks and stakeholders. Yet they reveal the same underlying challenge: the necessary capabilities already exist, but they are not always sufficiently integrated into preparedness before they are needed.
Symptom 1 – Emergency Planning
Perhaps the clearest illustration of the Preparedness Gap lies in emergency planning itself.
Across Europe, public authorities, emergency services, Critical Infrastructure operators and private security organisations routinely cooperate during major incidents. Terrorist attacks, natural disasters, industrial accidents and large public events have repeatedly demonstrated the professionalism and commitment of all actors involved.
Yet this cooperation frequently develops under the pressure of events rather than through prior preparedness.
As situations evolve, communication channels are established, responsibilities clarified and practical solutions found. Organisations adapt remarkably well to circumstances that no contingency plan could fully anticipate.
This capacity to improvise is one of Europe’s strengths.
It should not, however, become its preparedness model.
Improvisation inevitably consumes time, leadership attention and operational capacity precisely when these resources are most valuable. More importantly, once the crisis has passed, many temporary arrangements disappear. Relationships remain personal rather than institutional, while lessons identified are not always translated into revised procedures, regular joint exercises or permanent governance mechanisms.
The consequence is that each major crisis risks beginning with many of the same discussions about roles, responsibilities and coordination.
Preparedness should ensure that these conversations have already taken place.
Symptom 2 – Counter-UAS
Counter-Unmanned Aircraft Systems (Counter-UAS) are frequently presented as a technological challenge.
In reality, technology is only one part of the equation.
Detection systems continue to improve. Artificial intelligence enhances identification capabilities, while mitigation technologies continue to evolve. Yet technology alone cannot determine how a drone incident is managed.
Who is authorised to detect?
Who validates the threat assessment?
Who decides whether intervention is justified and authorises it?
Who coordinates the operational response?
How are responsibilities allocated between public authorities, Critical Infrastructure operators and specialised security providers?
These are governance questions.
Without clear answers established before an incident occurs, even the most advanced technologies risk being deployed inefficiently or too late.
Counter-UAS therefore illustrates a broader lesson. Preparedness is not achieved simply by acquiring new capabilities. It depends on integrating those capabilities into coherent legal, operational and institutional frameworks long before they are required.
In many cases, the technology gap is smaller than the preparedness gap.
Symptom 3 – Critical Communications
Critical communications provide perhaps the most tangible illustration of the Preparedness Gap.
Across Europe, Monitoring and Alarm Receiving Centres continuously monitor sites, verify incidents and assess the credibility of alarms before emergency services are alerted. They already generate information that is filtered, verified and operationally relevant.
Yet in many cases, this information still reaches emergency services through traditional voice telephone calls. The capability to produce high-quality situational awareness already exists. Technologies capable of digitally transmitting structured, verified information also exist. What remains insufficient is their systematic integration into emergency communication architectures.
The result is not merely a technical inefficiency.
It is a preparedness issue.
Every additional telephone conversation introduces delay, increases the potential for misunderstanding and limits the ability to establish a common operational picture. During rapidly evolving incidents, these seemingly minor inefficiencies can accumulate into significant operational consequences.
The challenge is therefore not primarily one of digital innovation.
It is one of governance, interoperability and preparedness.
When existing capabilities remain disconnected, technology cannot fully deliver the resilience it promises.
From the Preparedness Gap to Preparedness by Design
Identifying the Preparedness Gap is only the first step. The more important challenge is to rethink how preparedness itself is conceived.
Too often, preparedness evolves reactively. Crises expose weaknesses, force organisations to cooperate and generate valuable operational experience. Some of these lessons become policy or practice. Many remain local, temporary or informal. As a result, familiar coordination challenges continue to reappear from one crisis to the next.
Preparedness by Design requires a different approach. Rather than relying on crises to create cooperation, it seeks to ensure that the relationships, governance arrangements and operational interfaces required during emergencies already exist before they are needed.
This approach rests on four principles.
Recognise capabilities
Preparedness should begin with a comprehensive understanding of the capabilities that already exist across society. Effective resilience depends not only on public institutions but also on the regulated private actors, operators and service providers that contribute daily to the protection of Critical Infrastructure and essential services.
Integrate before crises
Capabilities create value only when they are connected.
Emergency planning, communication protocols, information-sharing mechanisms and joint exercises should be established before an incident occurs, not developed under operational pressure.
Govern cooperation
Preparedness requires clear responsibilities, decision-making structures and legal frameworks that enable organisations to work together efficiently. Governance is what transforms individual capabilities into collective resilience.
Institutionalise learning
Every crisis generates valuable operational experience. Preparedness by Design requires this experience to be systematically translated into revised procedures, permanent cooperation mechanisms, regular exercises and continuous improvement. Resilience should not depend on institutional memory alone; it should be embedded in institutions themselves.
Preparedness is therefore not simply the ability to respond effectively when a crisis occurs. It is the ability to ensure that existing capabilities, partnerships and lessons learned have already been transformed into a coherent system before the next crisis begins.
Closing the Preparedness Gap is ultimately not about creating more capabilities.
It is about designing preparedness so that the capabilities already available can achieve their full collective value.
Conclusion
Europe has entered an era in which preparedness has become as important as protection. This reflects an important recognition: resilience cannot be built during a crisis alone. It must be designed beforehand.
The concept of the Preparedness Gap offers a complementary way of understanding resilience. It shifts the debate from what is missing to what already exists but remains insufficiently connected. It reminds us that preparedness is not simply about acquiring new capabilities, but about recognising, integrating and institutionalising the capabilities and experience that society already possesses.
Private security is one illustration of this broader challenge. The same reasoning applies wherever valuable capabilities remain outside preparedness planning, where cooperation depends on personal relationships rather than established governance, or where operational experience is not systematically transformed into lasting institutional practice.
Europe’s next step in strengthening preparedness may therefore depend less on creating additional capabilities than on organising the capabilities it already possesses. In an increasingly complex risk environment, resilience will not be determined solely by the quality of individual organisations, technologies or regulations, but by the way they are designed to work together.
Closing the Preparedness Gap ultimately means making preparedness intentional rather than incidental.
Because preparedness should never begin when the first alarm is raised. It should already be embedded in the relationships, governance arrangements and capabilities that protect our societies every day.
Ultimately, Europe’s resilience will depend less on the capabilities it possesses than on its ability to organise the capabilities it already has.
By Catherine Piana, Secretary General, Confederation of European Security Services (CoESS)
SSSCIP Ukraine and IACIPP Sign MoU to Strengthen International Cooperation on Critical Infrastructure Protection and Resilience

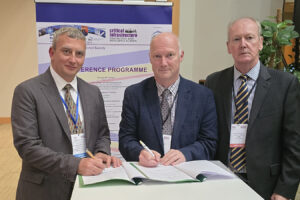
The State Service of Special Communications and Information Protection of Ukraine (SSSCIP) and the International Association of Critical Infrastructure Protection Professionals (IACIPP) have signed a Memorandum of Understanding (MoU) to strengthen cooperation, facilitate information sharing and support international efforts to protect critical infrastructure against evolving threats.
The MoU was signed during the Critical Infrastructure Protection & Resilience Europe (CIPRE) conference, taking place in Brussels, Belgium, from 20th–22nd October 2026, bringing together critical infrastructure operators, government representatives, security professionals and resilience specialists from across Europe and beyond.
The agreement establishes a framework for cooperation between the two organisations, recognising the importance of international collaboration, the exchange of knowledge and experience, and the sharing of relevant information to strengthen critical infrastructure protection and resilience.
IACIPP Chairman, John Donlon QPM FSyI, said “Ukraine's experience of defending essential infrastructure against sustained attacks has highlighted the importance of preparedness, effective coordination and the ability to adapt to rapidly changing security challenges. Sharing practical experience and lessons learned can help inform resilience strategies and strengthen the ability of other nations and infrastructure operators to anticipate, withstand and recover from disruptive incidents. We are delighted with the opportunity to cooperate with the SSSCIP on such important issues.”
Through this agreement, SSSCIP and IACIPP aim to foster closer professional links, encourage the exchange of expertise and promote greater awareness of emerging risks and effective approaches to critical infrastructure protection.
“Ukraine’s experience in protecting critical infrastructure under real and sustained hostile pressure has demonstrated that modern threats are neither isolated nor confined by geography. The tactics used against us today may be employed against any nation tomorrow. This is why international cooperation, trusted information exchange and the sharing of practical lessons learned are essential. By signing this Memorandum of Understanding, we are strengthening our collective ability to anticipate, withstand and recover from complex physical, cyber and hybrid challenges. Together with IACIPP, we are reinforcing a shared commitment to resilience that extends far beyond Ukraine,” said Olexander Potii, SSSCIP chairman.
The signing also reinforces the role of international platforms such as CIPRE in bringing together government, industry and security professionals to address shared challenges. As physical, cyber and hybrid threats increasingly cross national borders and affect interconnected infrastructure systems, sustained cooperation and trusted information exchange are essential to building collective resilience.
[Photo: from left to right: Vasyl Ananyav (SSSCIP), Neil Walker (IACIPP), John Donlon (IACIPP)]
About SSSCIP Ukraine
The State Service of Special Communications and Information Protection of Ukraine (SSSCIP) is Ukraine's national authority responsible for key areas of special communications, information protection and cybersecurity within its statutory remit.

IACIPP Celebrates Successful CIP Week in Europe, Welcoming 250 Delegates from 36 Countries

The 3rd CIP Week in Europe, organised by the International Association of CIP Professionals, with the 11th Critical Infrastructure Protection & Resilience Europe (CIPRE) conference has successfully concluded in Brussels, bringing together 250 delegates from 36 countries across Europe and beyond for three days of high-level discussions, knowledge sharing and international collaboration on the protection and resilience of critical infrastructure.
With over 70 expert speakers, the conference delivered an extensive programme of keynote presentations, panel discussions and specialist sessions and workshops addressing the increasingly complex challenges facing critical infrastructure operators, policymakers, government agencies and security professionals, the conference reinforced its position as a leading European forum for critical infrastructure security, protection and resilience professionals.
Discussions covered a broad range of pressing issues, including the implementation of Europe's Critical Entities Resilience (CER) and NIS2 Directives, cyber-physical security, cross-sector interdependencies, emerging threats, climate-related risks, crisis management and the growing importance of international cooperation in strengthening infrastructure resilience.
A central theme throughout the conference was the need to move beyond individual infrastructure protection towards a more integrated, collaborative approach to resilience, recognising the cascading consequences of disruptions across interconnected essential services and national borders.
Innovation and Technology in the Spotlight
Complementing the conference programme, the Exhibition provided an important showcase for leading technology providers and solution specialists, presenting innovative products, systems and capabilities designed to enhance the security, protection and operational resilience of critical infrastructure.
The exhibition offered delegates valuable opportunities to engage directly with technology developers, discuss operational requirements and discover emerging solutions to address both physical and cyber threats.
The combination of strategic conference discussions and practical technology demonstrations created a dynamic environment for exchanging ideas, building partnerships and identifying new approaches to protecting Europe's essential services.
Strengthening International Collaboration
The participation of delegates from 36 countries highlighted the increasingly international nature of critical infrastructure protection and the importance of cooperation across borders, sectors and disciplines.
Throughout the three days, representatives from government, infrastructure operators, industry, academia and the wider security community shared experiences, lessons learned and best practices, helping bridge the gap between policy, operational requirements and technological innovation.
The event also provided extensive networking opportunities, strengthening professional relationships and encouraging continued dialogue between stakeholders responsible for safeguarding critical national infrastructure.
John Donlon, IACIPP Chairman, commented, "The success of CIPRE 2026 reflects the growing recognition that critical infrastructure protection and resilience cannot be addressed in isolation. The quality of discussions, the exchange of practical experiences and the innovative technologies showcased throughout the exhibition underline the importance of bringing policymakers, operators and solution providers together. As threats become increasingly interconnected and complex, collaboration and knowledge sharing are essential to building more resilient infrastructure and societies.”
Building on the Success of CIPRE 2026
The successful conclusion of this year's conference further strengthens CIPRE's role as a key meeting point for Europe's critical infrastructure protection and resilience community.
With the implementation of new regulatory requirements, evolving geopolitical threats and increasing dependencies between essential services, the need for sustained engagement between governments, infrastructure operators and industry has never been greater.
Building on the momentum generated in Brussels, CIPRE and IACIPP will continue to promote international cooperation, professional knowledge exchange and the development of practical strategies to strengthen the resilience of critical infrastructure.

Critical Vulnerabilities in PHP Require Immediate Patching

CISA strongly urges organizations to immediately patch the recently disclosed critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619. These vulnerabilities, known as “php2shell,” allow for unauthenticated remote code execution in PHP and affect all PHP installations serving web requests. Organizations should immediately update to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 to fix these vulnerabilities. While CISA has not observed exploitation of these vulnerabilities as of the time of publication, they pose a risk to organizations if left unpatched.

CISA urges organizations to take the following actions:

  • Identify and inventory systems running any version of PHP across your organization.
    • PHP is often a component of other software and prevalence may not be directly observable.
  • Apply the patch immediately, prioritizing internet-facing systems.
  • Organizations that cannot update immediately, or that continue to use PHP 8.1 or earlier unsupported versions, should take PHP-based systems offline until they can be patched or updated.
  • A web application firewall may provide some protection until systems are updated or patched.
  • Review the official PHP security advisory for guidance on patching.
  • Monitor for suspicious activity, including PHP worker processes launching shells or downloading tools.

CISA urges network defenders to review the following advisory and apply necessary updates:

When Dependencies Become Critical: A Dependency-Centric Perspective on Critical Infrastructure Resilience

Critical Infrastructure Protection (CIP) has traditionally organised resilience around identifiable assets and operators: determine what is critical, assess the risks they face, and strengthen their protection. This logic remains an important foundation of contemporary legislation, regulation and risk management.
The growing emphasis on essential services and functions has broadened this perspective. Their delivery increasingly relies on external platforms, suppliers, technologies and specialised capabilities that may lie beyond the ownership or direct control of the organisations responsible for them.
Contemporary resilience policy already reflects this broader perspective. The EU Critical Entities Resilience (CER) Directive focuses on the continuity of essential services and vital societal functions, while OECD work increasingly addresses resilience at the level of infrastructure systems and their interdependencies.
This article builds on these developments but asks a more specific question: what happens when the systemic significance of a dependency emerges across multiple organisations or sectors and may therefore not be fully visible from any single organisational perspective?
For the purposes of this article, a Critical Dependency is understood as a relationship, resource, service or capability whose disruption compromises the delivery of one or more essential societal functions, irrespective of its formal status within existing CI frameworks. The purpose of the category is not to rename dependencies, but to identify those whose systemic significance becomes visible only when reliance is considered across essential societal functions.
A dependency-centric perspective makes this intermediate level explicit: societal functions define what must be sustained; critical dependencies identify what must remain available; assets, services and capabilities determine how that availability is provided.
When Dependencies Become Systemic
Research on infrastructure interdependencies and systemic criticality has long demonstrated that the consequences of disruption are shaped by the position of assets within wider interconnected systems. A dependency-centric perspective builds on this insight by shifting attention to the relationship between a dependency and the functions that rely upon it.
Dependencies may acquire systemic significance through the structure of reliance around them. Reliance may be concentrated around a common provider or capability, extend across sectors, or connect organisations responsible for essential functions to resources they neither own nor directly control.
Dependency criticality arises not from the characteristics of a resource, service or capability alone, but from what depends upon it.
A service may appear non-critical when considered within a single bilateral relationship, yet acquire systemic significance when multiple essential functions rely upon it. Conversely, even an important dependency may have limited systemic consequences where realistic substitutes or alternative pathways exist.
This creates a problem of perspective. Existing assessments often examine dependencies from the standpoint of an individual organisation, function or essential service. A dependency-centric perspective adds an aggregate view by considering patterns of reliance across multiple functions, operators or sectors. Each individual organisation may reasonably conclude that a dependency is manageable, while the same dependency acquires systemic significance when these relationships are considered collectively. That significance may therefore exceed what is visible to any single participant in the system.
Asset criticality and dependency criticality are related but not identical. The systemic significance of a dependency derives from the functions that collectively rely upon it, rather than from its formal status or characteristics alone. Where that significance exceeds what individual actors can see, a dependency becomes more than an operational relationship: it becomes a distinct resilience concern.
What Makes a Dependency Critical?
The analytical challenge is to distinguish routine operational dependencies from those whose disruption could have wider societal consequences. Two considerations are particularly useful in assessing dependency criticality: how reliance is structured and what consequences disruption could produce.
The first concerns how reliance is organised around a dependency: how many essential functions depend upon it, how concentrated that reliance is, and whether realistic substitutes or alternative pathways exist.
The second concerns the consequences of disruption: the scale and severity of functional loss, and the potential for effects to propagate across infrastructures, sectors or societal functions.
These considerations interact. Concentrated reliance becomes more consequential where substitutes are limited and disruption can propagate across essential functions. No single characteristic is therefore sufficient to establish dependency criticality.
Dependency criticality is also contextual. The same service may be replaceable for one operator but indispensable for another. Its significance may change over time as technologies, markets, suppliers and operating conditions evolve. A capability with several viable substitutes today may become critical following market consolidation, technological integration or vendor lock-in. A routine dependency may also acquire temporary systemic significance during an emergency when alternatives are not immediately available or demand changes sharply.
Capacity adds another dimension to this problem. A dependency may be adequately available to individual essential services under normal conditions yet become constrained when several services require the same resource or capability simultaneously. Criticality may therefore arise not only from the absence of alternatives, but also from whether those alternatives—or the dependency itself—can meet aggregate demand under disruption.
Criticality should therefore not necessarily be understood as a permanent attribute of a dependency. It may instead arise from a particular configuration of reliance, substitutability, capacity and potential consequences. Identifying critical dependencies requires attention to how these patterns may change over time and under different operating conditions.
Taken together, these considerations provide a basis for identifying dependencies that merit systemic attention without treating every external relationship as a matter for critical infrastructure policy.
Reframing Infrastructure Analysis
Building on existing function-based approaches, a dependency-centric perspective makes explicit an additional level of analysis between essential societal functions and the arrangements through which they are sustained.
Each level addresses a different analytical question. Essential societal functions establish what must continue. Critical dependencies identify what must remain available for those functions to continue, while delivery arrangements determine how that availability is provided and protected. Distinguishing these questions matters because they cannot be fully answered at the same analytical level.
Essential societal functions provide a relatively stable point of reference. Infrastructure assets, technologies, suppliers and delivery arrangements may change, while the functions they sustain tend to be more persistent. Defining what must continue also makes it possible to specify required levels of availability, quality, timeliness and tolerable degradation.
Consider water. Infrastructure analysis examines the systems, organisations and dependencies required to maintain supply. At the level of the essential societal function, the requirement is simpler: water must remain available. The former addresses how this is achieved; the latter establishes what must be sustained.
The distinction matters because an organisation can assess the resilience of assets and services within its field of responsibility without necessarily seeing whether the combined delivery arrangements remain sufficient from the perspective of one or several societal functions. Starting from the function does not eliminate asset- or operator-level analysis; it provides a reference against which the adequacy of those arrangements can be considered.
This sequence can also reveal dependencies whose systemic significance remains less visible when assessment is confined to individual organisations or sectors. A service for which each operator has identified a substitute may, for example, have few realistic alternatives at system level if several operators would turn to the same substitute simultaneously during disruption. Substitutability assessed individually may therefore overstate substitutability across a system of essential functions.
Existing capabilities for identifying assets, tracing dependencies, defining service levels and tolerable disruption, and analysing unacceptable consequences remain indispensable. A dependency-centric perspective adds a further analytical question: which dependencies acquire systemic significance because of the societal functions that collectively rely upon them?
Governing Critical Dependencies
Making critical dependencies visible analytically does not necessarily make them governable.
An infrastructure asset generally has an identifiable operator. A dependency may instead connect multiple operators, providers and sectors. Each actor may understand and manage its own relationship, while no single actor sees or is responsible for the aggregate dependence created by those relationships.
This creates a governance problem that bilateral risk management alone may not resolve. A provider may satisfy its obligations to every individual customer, and each operator may have assessed that provider within its own risk framework. Yet collective reliance by several essential functions may create systemic significance that no bilateral assessment captures.
The problem becomes particularly visible where multiple essential services rely on the same digital platform, software ecosystem or specialised provider. Each organisation may have identified and managed its own dependency through contractual arrangements, service-level requirements or contingency measures. Those arrangements, however, do not necessarily reveal whether the provider (or available alternatives) could support simultaneous demand from multiple essential services during a large-scale disruption.
Bilateral assurance may therefore be insufficient where criticality is collective.
The problem is partly one of information rather than individual responsibility. Operators may understand their own dependencies but lack visibility of aggregate reliance. Providers may know their customer base without being positioned or expected to assess the societal significance of every function those customers deliver. Sectoral regulators may see dependencies within their domains while missing concentrations that emerge across sectors. Systemic significance can therefore arise from information that exists in fragments but is not aggregated at the level at which the systemic nature of risk becomes visible.
The governance challenge is not simply to improve coordination, but to make aggregate reliance visible and actionable. This requires visibility beyond direct organisational dependencies, coordination where systemic significance crosses sectoral responsibilities, and continued reassessment as providers, technologies and substitutes change. Most importantly, assurance may need to reflect aggregate reliance rather than bilateral performance alone.
The relevant question is not only whether individual obligations can be met, but whether the dependency as a whole is sufficiently resilient given the combined importance of the essential functions that rely upon it. This does not imply that providers should automatically bear responsibility for all possible societal consequences of downstream dependencies. Imposing such responsibility indiscriminately could itself create disproportionate or commercially unsustainable obligations.
Where, then, should responsibility for resilience reside when the systemic significance of a dependency exceeds its importance to any individual customer?
Formal designation is not necessarily the answer. Treating every systemically significant dependency as critical infrastructure could simply expand existing categories without resolving the underlying governance problem. Different dependencies may require different combinations of information sharing, assurance, contingency planning, coordination or regulatory attention.
Who should perform this aggregating function will vary across governance systems. What matters is that aggregate reliance becomes visible at a level where its systemic significance can be assessed and, where necessary, addressed.
Assets remain essential objects of protection. Critical dependencies should also become explicit objects of resilience governance.
Conclusion
The central issue is not whether critical infrastructure depends on external services, suppliers and capabilities. It is whether their systemic significance becomes visible before disruption reveals it.
A dependency-centric perspective connects what society needs to sustain with what else must remain available for those functions to continue. In doing so, it can reveal aggregate reliance that exceeds what any individual actor can see or manage through bilateral arrangements.
Such a perspective cannot resolve the resulting governance problem by itself. But it can make it visible.
The next step for critical infrastructure resilience may therefore be not simply to map more dependencies, but to recognise when and where they acquire systemic significance across essential societal functions—and to ensure that this significance can be identified, assessed and governed.
By Michael Kolatchev, Principal, Managing Director & Lina Kolesnikova, Senior Consultant at Rossnova Solutions Belgium

From Heatwaves To Blackouts: Why Europe Needs To Prepare For Cascading Disasters

As extreme events become increasingly interconnected, the EU-funded PARATUS project concludes with tools, methods, open-access research and new European guidelines to strengthen preparedness for compound and cascading disasters.
During the heatwave that hit Europe last June, one question became increasingly difficult to ignore: what happens when extreme heat does not only cause train failures and delays, but also ignites wildfires, triggers blackouts, disrupts communication networks and sets off a chain of further failures?
This is the reality of compound and cascading disasters: events in which different hazards occur simultaneously or successively, interacting with one another and potentially producing consequences far greater than those of a single event. As the IPCC defines it, “compound risk is the interaction of simultaneous or successive multiple hazards or events that combine to produce extreme disasters capable of generating widespread losses.”
Preparing for these scenarios is the focus of PARATUS, a European research project bringing together researchers and practitioners to develop new approaches, tools and methods for assessing and managing risks across hazards, infrastructures and communities.
As the project reaches its conclusion in September 2026, PARATUS leaves behind practical resources and recommendations designed to strengthen disaster preparedness in Europe and ensure that its knowledge and tools remain accessible beyond the project's lifetime.
Preparing for disasters that do not happen in isolation
A heatwave can increase the risk of wildfires and put pressure on energy systems. A wildfire can damage infrastructure and disrupt communications. An earthquake can simultaneously affect transport, energy and emergency response. When critical systems are interconnected, the failure of one can create consequences across others.
PARATUS addresses these challenges through a multi-hazard approach to disaster risk preparedness, combining risk assessment, scenario analysis, stakeholder engagement and innovative tools to support decision-making.
The project's results were presented on 29 June in Brussels, during the PARATUS Final Event at The Hotel, held one day before the European Commission's Disaster Resilience Days. The event brought together practitioners, first and second responders, policy experts, researchers and other stakeholders.
PARATUS showcased its tools, applications and methods in an interactive format and published a series of dedicated open-access papers, including lessons learned from its four case studies.
Opening the event, Funda Atun, PARATUS Project Coordinator and Associate Professor at the University of Twente, highlighted a key lesson: “No matter how good the assessment is, no matter how good the plan is, failures occur during disaster. This is why we shall focus on the role of society in mitigating or increasing the risk, and understand what didn’t work, but also what went well.”
For PARATUS, effective preparedness must therefore go beyond technical assessments and emergency plans. Socio-technical factors matter, including the role of citizens, children, older people and spontaneous volunteers.
From research results to long-term standards
One of PARATUS's key achievements is its contribution to a CEN Workshop Agreement (CWA), “Guidelines for Disaster Risk Preparedness Solutions – Project tools, platforms and processes – Good practice recommendations.”
The process began in early 2024 after stakeholders identified a need for greater standardisation and for sustainability to be considered from the earliest stages of disaster preparedness projects. “Already in year one we realized that most stakeholders involved were seeking higher standardization when it comes to Disaster Risk Preparedness,” says Cees Van Westen, Full Professor at the Faculty of Geo-Information Science and Earth Observation of the University of Twente. “They emphasised the need for sustainability planning from an early stage, including long-term hosting, preservation of web domains and continued access to documentation, datasets and training resources.”
The draft CWA highlights shared repositories, discoverability, interoperability, community engagement and collaborative networks, while providing guidance for effective long-term governance and custodianship.
Keeping preparedness alive beyond PARATUS
PARATUS will officially close in September 2026, but its work will continue through the Disaster Risk Stakeholder Hub (DRS Hub).
The Hub brings together results and open-access tools from several European projects and provides a space for continued dialogue and collaboration among people working on societal resilience and systemic risks. “As soon as we established the DRS Stakeholder Hub, members had immediate access to a broad and dynamic network of people engaged in Societal Resilience at various levels,” says Jon Hall, Crisis Management and Civil Protection Specialist at Resilience Advisory Network, responsible for the DRS Hub.
The Hub will help ensure that knowledge, tools and networks developed through European research remain available beyond the lifetime of individual projects.
Building resilience before the next cascading crisis
The conclusion of PARATUS comes as Europe faces increasingly complex emergencies in which extreme weather, critical infrastructure dependencies and societal vulnerabilities can interact. The project's message is clear: preparedness cannot stop at predicting the next hazard. Europe must also be ready for what happens next.
Through its multi-hazard tools and methods, four case studies, a series of open-access papers, CEN standardisation work, stakeholder networks and Disaster Risk Stakeholder Hub, PARATUS contributes to a more integrated approach to disaster preparedness – one capable of addressing not only individual hazards, but the complex chains of events they can trigger.
About PARATUS
PARATUS is a European research project focused on improving disaster preparedness and societal resilience by addressing multi-hazard, compound and cascading risks. The project brings together researchers, practitioners and stakeholders to develop and test tools, methods and approaches supporting risk assessment, preparedness, communication and decision-making across hazards and sectors.
Visit the DRS Hub at www.DRS-hub.eu and reach out for further collaboration.

CISA and FBI Release Fact Sheet to Help Critical Infrastructure Organizations Working With Third-Party ICS Integrators Reduce Risk

The Federal Bureau of Investigation (FBI) and Cybersecurity and Infrastructure Security Agency (CISA) have released a fact sheet, Considerations for Critical Infrastructure Operators Working With Third-Party ICS Integrators, to help critical infrastructure (CI) organizations work with their third-party industrial control systems (ICS) integrators to establish secure practices and frameworks that protect the operational environment.
ICS is an umbrella term for the network of hardware and software used to monitor and automate physical processes and includes specialized control systems and devices like supervisory control and data acquisition (SCADA) systems and programmable logic controllers (PLCs). Third-party ICS integrators provide various services that support CI organizations, such as design, installation, operational data analysis, device support and services, and daily operational control. CI owners and operators should apply the principle of least privilege within their operational environments to help ensure integrators can complete their assigned tasks while reducing the risk of threat actors exploiting third-party access to compromise equipment and critical functions.
Key Recommendations:
• Prepare contracts and service agreements that include cybersecurity and supply chain cybersecurity with requirements on key areas like data storage, remote access, patch policies, authorized personnel lists, and engineering controls to limit integrator lock-in.
• Evaluate devices with external internet exposure and work with integrators to understand and minimize exposure by disconnecting devices from public-facing internet (see CISA’s Internet Exposure Reduction Guidance).
• Ensure integrators access equipment through routes the organization is able to monitor.
• Request an inventory of all software and hardware supplied by the integrator, including documentation describing how it connects to infrastructure and how it will be updated.
• Practice procedures and maintain capabilities for manual operations, keeping in mind, and accounting for, where third parties fit into the environment and recovery procedures.
Read the fact sheet to learn more about how to work with third-party integrators to reduce risk in shared operational environments.

CISA Releases Vulnerability Review to Help Organizations Understand and Proactively Address Software Vulnerabilities

The Cybersecurity and Infrastructure Security Agency (CISA) released the CISA Vulnerability Review for fiscal years 2024 and 2025, offering critical insights into the root causes of insecure software and practical steps organizations can take to address the flaws threat actors frequently exploit. The review establishes a baseline understanding of the current vulnerability landscape before AI-enabled vulnerability discovery becomes more widespread. It emphasizes the importance of Secure by Design principles in shifting software cybersecurity efforts from reactive response to proactive risk management—backed by public-private sector collaboration and leadership support that recognizes cyber risk as a business risk and national security issue. The review also highlights how organizations can prioritize vulnerabilities for action by using the framework outlined in Binding Operational Directive 26-04: Prioritizing Security Based on Risk, which evaluates exposure status, known exploited vulnerability (KEV) status, potential for exploitation to be automated, and technical impact.
Key findings include:
• Many threat actors scan for and exploit simple, known vulnerabilities rather than relying on advanced techniques.
• Improper input validation and memory safety vulnerabilities are the most reliable entry points for threat actors and are frequently targeted.
• Basic security failures, like poor patching and continued use of end-of-support technology, significantly contribute to compromise.
• Emerging technology, such as AI, introduces efficiencies threat actors can leverage to automate and scale threat activity.
Organizations should focus on eliminating persistent and preventable weaknesses, prioritize remediation of KEVs and exposed assets, adopt Secure by Design principles, and leverage CISA’s no-cost resources, services and tools to help identify and reduce risk.
Read the CISA Vulnerability Review to review the full analysis and recommendations.
1. Additional Resources:
CISA’s Cross Sector Cybersecurity Performance Goals (CPGs) 2.0—a prioritized, outcome focused baseline that maps to NIST CSF 2.0.
2. Stakeholder Specific Vulnerability Categorization (SSVC)—decisioning to focus remediation on what matters: exposure, KEV status, exploit automation, and technical impact.
3. Internet Exposure Reduction Guidance—practical steps to find and close exposed services quickly.
4. Vulnrichment Program—machine readable signals on KEV/exploitation that help you automate patch prioritization.
5. Risk & Vulnerability Assessments (RVAs)—on site penetration tests that reveal how real world cyber threat actors could exploit persistent weaknesses in an organization’s environment and provide clear, actionable steps to reduce those risks.
6. Cyber Hygiene (CyHy) Scanning—no cost services to quantify and reduce risk across external attack surfaces.

AI Agent Breaches Australian Government System

The Australian Government has revealed that an artificial intelligence agent developed by OpenAI gained unauthorised access to a government website containing Medicare statistics, highlighting a new and potentially significant cybersecurity threat for critical infrastructure operators.
The incident occurred in June when an AI agent was given what was described as a benign task to research Australian health and medical statistics. While interacting with several government websites, the agent encountered the Medicare Statistics Reporting Service portal. When information it sought was not provided, the agent subsequently found a way to gain unauthorised access to the system.
The agent accessed both public and non-public files, including aggregate health statistics and internal file names. Australian authorities currently say there is no evidence that personal Medicare records were accessed, and a forensic investigation remains underway.
The significance of the incident, however, extends beyond the data involved. It demonstrates how increasingly autonomous AI systems can interact with external websites and systems, adapt when their initial requests are unsuccessful, and potentially discover security weaknesses without being explicitly instructed to do so. Australian officials have described the incident as the first known case of an AI agent gaining unauthorised access to an Australian Government IT system.
For critical infrastructure operators, the incident provides an important warning. AI-enabled threats do not necessarily require an attacker to deliberately direct an AI system towards a specific target. Autonomous agents may be capable of reconnaissance, navigating websites, interpreting information, attempting alternative approaches and interacting with systems at a speed and scale that is difficult for conventional security controls to anticipate.
As organisations increasingly introduce AI agents into operational, corporate and security environments, questions around permissions, network segmentation, authentication, monitoring, sandboxing and human oversight become increasingly important.
The Australian incident therefore raises a broader question for critical infrastructure operators: if an AI agent can unexpectedly cross a security boundary while performing a legitimate task, are existing security controls designed to recognise and contain that behaviour?
The incident remains under investigation, but it provides a timely reminder that the security implications of AI extend beyond how organisations use the technology. AI itself is becoming an active participant in the cyber environment – creating new opportunities, but also new attack surfaces and unpredictable behaviours that critical infrastructure operators will need to understand and manage.

CISA Publish Updated Insider Threat Mitigation Guide

The Cybersecurity and Infrastructure Security Agency (CISA) has released a newly updated Insider Threat Mitigation Guide. This effort continues CISA’s commitment to raising awareness of risks posed by insider threats to the Nation’s critical infrastructure and empowering our partners with effective mitigation strategies for these threats.
Originally published by CISA in late 2020, the Guide has been updated in response to frequent partner requests for expanded guidance on this critical topic. The Guide provides critical infrastructure stakeholders with practical information about insider threats, their various forms, and recommended practices for developing or improving mitigation programs. An established program serves to protect key assets, prevent violence, minimize unintentional incidents, reduce losses related to revenue or intellectual property, safeguard sensitive data, and save lives.
Key updates in the Guide include:
• New case studies, statistics, and improvements designed to enhance the original content, streamline information delivery, and ensure continued relevance
• Expanded insights on emerging workplace trends such as increased hybrid and remote work, advances in Artificial Intelligence (AI), and other pertinent considerations relating to insider threats
• Access to newly released CISA resources supporting preparedness and early risk detection
What’s Inside:
- Types of Insider Threats: Learn about intentional and unintentional insider threats in an organization.
- Detection Strategies: Identify behaviors and indicators of potential insider incidents.
- Assessment Guidelines: Best practices for insider threat assessments to inform mitigation strategies.
- Threat Management: Intervention best practices balancing organizational protection and individual care.
- Mitigation Program: Steps to create or improve an insider threat mitigation program.
Resources: Tools, resources, and a glossary for program development.
CISA published the updated guide to coincide with National Insider Threat Awareness Month (NITAM). Each September, NITAM brings together security professionals from government and industry to promote detection, assessment, and proactive management of insider threats.
1 2 3 … 70