CISA Announces Revised Town Hall Schedule to Engage with Stakeholders on Cyber Incident Reporting for Critical Infrastructure

The Cybersecurity and Infrastructure Security Agency (CISA) today announced a revised schedule for a series of virtual town hall meetings to gather stakeholder input on the Cyber Incident Reporting for Critical Infrastructure Act of 2022 (CIRCIA) rulemaking. Scheduled to begin June 15, these town hall meetings replace the town hall meetings previously scheduled for March and April 2026, but which CISA was not able to hold due to the recent Democrat shutdown of the Department of Homeland Security (DHS).
CISA remains committed to affording stakeholders the opportunity to provide additional input on the CIRCIA rulemaking through a town hall series before the rule is finalized. The revised schedule is available in the Federal Register. Interested stakeholders may register for the town hall meetings at www.cisa.gov/circia. Any changes or updates to the town halls will be available on www.cisa.gov/circia.
“CISA is working to maximize the impact of CIRCIA to significantly improve our Nation’s cybersecurity posture. At the same time, CISA values the interest and concern our stakeholders have that CIRCIA will be implemented with minimal unnecessary burden to entities in critical infrastructure sectors,” said CISA Acting Director Nick Andersen. “CISA appreciates our stakeholder’s patience with waiting for our rescheduled town hall meetings to provide their critical input as we finalize this rule. As an agency built on collaboration and coordination, CISA is committed to hearing from the American people, critical infrastructure owners and operators, and other community members.”
CIRCIA is a U.S. law that will help the government quickly respond to cyber threats and share information to protect critical infrastructure. Once the final rule is implemented, covered organizations will be required to report certain cyber incidents to CISA within 72 hours and ransom payments within 24 hours.
CISA has received numerous requests for additional engagement on the CIRCIA rulemaking process and greatly values its stakeholders’ interest in shaping a final rule that maximizes CIRCIA’s impact on our Nation’s cybersecurity posture while minimizing unnecessary burden. Given the broad stakeholder community that CIRCIA may potentially impact, CISA will conduct a series of town hall meetings to solicit input on the Notice of Proposed Rulemaking (NPRM). CISA selected this approach to gather additional engagement on the CIRCIA NPRM to provide access to CISA across the broad range of entities within the critical infrastructure sectors.
CISA issued the CIRCIA NPRM in April 2024. To inform the CIRCIA NPRM, CISA hosted in-person public listening sessions across the country, conducted virtual sector-specific sessions, and engaged with Sector Risk Management Agencies (SRMAs) and other federal partners—all aimed at gathering meaningful input from a broad range of stakeholders. The NPRM was open for a 90-day public comment period.

NIS360: The bigger picture on maturity and criticality of NIS critical sectors

This year’s edition of the ENISA NIS360 report shows improvement in cybersecurity maturity of EU critical sectors while the level of criticality in sectors remains comparatively more stable.
The ENISA NIS360 aims to work as an annual assessment tool supporting national authorities, policymakers and other stakeholders in assessing the cybersecurity maturity and criticality of high criticality sectors under the NIS2 Directive.
ENISA Executive Director, Juhan Lepassaar, said: “The findings of this NIS360 report provide grounds to be optimistic. The implementation of the comprehensive EU cybersecurity regulatory framework, and particularly NIS2, has brought significant improvements. ENISA stands for prioritising cybersecurity and advancing the implementation of EU policies, which are vital now more than ever, to enhance the cyber resilience of our critical infrastructure and societies.”.
The report has a comprehensive approach, where each sector is understood to comprise relevant actors (i.e., national authorities, entities, EU bodies) and applicable rules (EU legislation). In this regard, a sector’s maturity under the NIS360 is determined by: legislation and its effectiveness, companies and their preparedness, authorities and their institutional capacity, and sectoral ecosystem structures and their effectiveness.
The assessment relies on a structured methodology developed and continuously refined by ENISA that takes into account the structural and gradually evolving nature of sectoral cybersecurity maturity and criticality. It also builds on evidence gathered over time from organisations operating within the in-scope sectors, national authorities supervising those organisations, but also EU-level data, to reflect our latest evidence-informed understanding of where each sector stands.
As a result, the NIS360 provides both a comparative overview of sectors and a more detailed analysis per sector to help identify gaps and prioritise resources.
Defining the Risk Zone
NIS360 sector risk zone
A combination and joint interpretation of the criticality and maturity dimensions helps identify areas where mismatches exist between the two and define a risk zone.
The risk zone includes sectors with lower-than-average maturity and criticality that exceeds their maturity. This year’s risk zone includes health, railway, maritime, ICT management service, space, public administrations, drinking and waste water.
Its composition changes over time as overall maturity improves across sectors. This explains why three sectors — railway, drinking water, and waste water — previously at the risk zone boundary, are now within the risk zone. A positive development is that the gas sector has started moving out of the risk zone.
Such shift is driven by improved information sharing, stronger collaboration, and better implementation of risk management measures, leading to higher maturity.
Deep-dive on criticality
While criticality of the sectors is defined by NIS2, the NIS360 assessment ranks the sectors taking into account several elements, such as systemic relevance, exposure, and impact of disruption. As these factors typically change gradually, criticality scores tend to remain relatively stable from year to year.
In this year’s edition, sectors such as banking, electricity, aviation, space, and digital-by-default services (including telecommunications, cloud, and data centres) remain the most critical.
Space has joined this group this year, reflecting its growing role in society and across other sectors, which increases dependency, impact, and time criticality. The railway sector increased in criticality due to its growing role in military logistics, and the heightened cyber threat exposure.
Spotlight on maturity 
Maturity is measured by how effectively and consistently the sector manages cybersecurity risks and capabilities over time, meaning the overall preparedness of the sector. Since the previous edition of this report, cybersecurity maturity across EU critical sectors seems to be steadily improving as organisations respond to the evolving policy requirements and to the cyber threats they face.
Three sectors, including trust services, aviation, and financial market infrastructures (FMIs) moved into the high maturity band. In addition, four sectors strengthened their maturity within the moderate band: gas, road, maritime, and health.
This improvement is often driven by several compounding factors including developments in cybersecurity legislation, increased political attention, but also progress across specific maturity dimensions assessed. Particularly, on cybersecurity legislation, findings of the 2025 ENISA NIS Investments study also suggest that it has acted as a key driver for cybersecurity investment and has encouraged organisations to strengthen their cybersecurity posture.
Despite maturity steadily improving across critical sectors, progress still remains uneven both across and within sectors. A number of factors contribute to these variations including skill shortages, sector-specific characteristics and even organisational size.
Moving forward
In the future, it is anticipated that cybersecurity legislation and organisations’ efforts to strengthen their cybersecurity maturity will continue to prompt cybersecurity investment and drive preparedness, leading to more sectors moving out of the risk zone.

Euro-Mediterranean partners advance cooperation on civil protection and disaster risk management

Representatives from across the Euro-Mediterranean region gathered this week for the Union for the Mediterranean (UfM) Civil Protection Meeting to advance regional cooperation on disaster risk management and support the implementation of the 2030 UfM Action Plan on Civil Protection and Disaster Risk Management.
The meeting brought together representatives from UfM Member States, the European Commission’s Directorate-General for European Civil Protection and Humanitarian Aid Operations (DG ECHO), the Prevention, Preparedness and Response to Natural and Man-made Disasters in the Mediterranean programme (PPRD Med), the International Federation of Red Cross and Red Crescent Societies (IFRC), and the United Nations Office for Disaster Risk Reduction (UNDRR). Discussions focused on strengthening regional collaboration on prevention, preparedness, response and recovery in the face of increasingly complex and interconnected risks across the Mediterranean region.
Advancing a shared vision for regional resilience
Participants reviewed recent progress under the UfM Civil Protection and Disaster Risk Management mandate and discussed priorities for strengthening regional cooperation through the UfM Regional Dialogue Platform.
The meeting highlighted key elements of the 2030 UfM Action Plan, including:
- Strengthening public awareness and volunteer engagement
- Enhancing preparedness through capacity development
- Supporting regional disaster assistance and cooperation
- Strengthening national and regional institutions
- Promoting monitoring, evaluation and learning
Discussions emphasized the importance of creating a common culture of risk awareness and resilience, while supporting closer cooperation among governments, civil society, technical institutions, and regional partners.
Strengthening preparedness and knowledge exchange
Participants shared experiences and initiatives aimed at strengthening preparedness and operational readiness across the Mediterranean region.
Discussions highlighted the importance of investing in prevention and preparedness, particularly as countries across the region face increasingly complex and interconnected risks, including wildfires, floods, earthquakes, and climate-related hazards.
Key areas of discussion included:
- Lessons from the 3rd Euro-Mediterranean High-Level Workshop on Fire Risks
- Volunteering and community engagement in disaster risk management
- Early warning systems and information sharing
- Capacity development and training opportunities
- Regional platforms for cooperation and knowledge exchange
Participants also explored opportunities to strengthen collaboration among civil protection authorities and regional partners, while advancing practical approaches to preparedness, information sharing, and mutual support across the Mediterranean.
Building momentum for regional action
UNDRR presented the Stop Disaster Game initiative (an educational tool that helps users better understand disaster risks and resilience-building measures) as an example of innovative approaches to strengthen disaster risk awareness and preparedness.
Participants further discussed opportunities to leverage regional platforms and initiatives, including UfM Med Green Week, to promote collaboration and strengthen engagement on disaster risk reduction and climate resilience.
Looking ahead
The meeting concluded with a shared commitment to continue advancing the implementation of the 2030 UfM Action Plan and strengthening cooperation among Euro-Mediterranean partners.
As countries across the region face increasing risks from wildfires, floods, earthquakes, droughts and other climate-related hazards, continued efforts to strengthen cooperation, preparedness, and operational coordination will help lay the foundations for a more resilient and interconnected Mediterranean.

When Cyber Attacks Reach the Physical World: The Growing Insurance Gap in Critical Infrastructure

Modern life depends on systems we rarely see. Power stations keep the lights on. Pipelines carry fuel across long distances. Chemical plants manage fast and complex reactions. Transport networks move people and goods every day.
Behind all of this sits Operational Technology (OT). These are the control systems, sensors and safety tools that keep physical processes running safely.
For many years, these systems were built with one aim: to keep operations stable. Cyber security was not a priority. Most OT systems were isolated, used proprietary technology, and were run by engineers rather than IT teams.
That world has changed.
Industrial systems are now connected to corporate networks, cloud platforms, remote access tools and supply chains. This has improved efficiency, but it has also created a new kind of risk: cyber attacks that affect the physical world.
When this happens, the impact is very different from a typical IT breach. Instead of lost data or downtime, the result can be damaged equipment, fires, explosions, pollution or long outages.
These events are still rare. But when they happen, the consequences can be severe.
The Nature of OT Cyber Risk
OT systems operate under the laws of physics.
They are designed to keep things like pressure, temperature and flow within safe limits. If those limits are exceeded, equipment can fail, sometimes in dramatic ways. That is why safety systems are built into industrial sites.
Cyber attacks can interfere with these safeguards. Any programmable safeguard designed for an intended function, can be re-programmed to behave in an unintended way.
Attackers might change sensor readings so operators think everything is normal. They might alter controls to change how machines behave. They could disable alarms or safety shutdown systems. In some cases, they may lock operators out of the system altogether.
In many cases, small changes can have big effects. Adjusting a valve, motor speed or sensor reading can push a system outside safe limits. Once that happens, problems can spread quickly.
What matters most is this: once a system crosses a safety boundary, physics takes over. Equipment will behave according to physical forces, not human intent.
How Attacks Reach Physical Systems
Most cyber-physical incidents do not start in the control room.
They often begin with standard IT breaches. A phishing email, stolen login details, weak remote access or a third-party connection can give attackers a foothold. From there, they move through the network until they reach systems linked to industrial processes.
This pattern has been seen before.
A well-known example is the 2014 attack on a German steel mill. Reports suggest attackers entered through the corporate network using phishing. They then moved into the plant’s control systems.
The disruption meant the plant could not safely shut down a blast furnace. This led to serious physical damage.
The lesson is clear: an IT issue can become a physical incident once attackers cross into OT systems.
Not all attacks are highly advanced.
In Australia, a former contractor used radio signals to control sewage pumps, releasing waste into public areas. In Poland, a teenager reportedly used a simple device to interfere with tram systems.
These cases show that even basic weaknesses—like poor access controls or exposed systems—can lead to real-world damage.
Near Misses and Hidden Risks
Some of the most important warnings come from incidents where disaster was narrowly avoided.
The Triton malware attack in Saudi Arabia is a key example. The attackers targeted a system designed to prevent serious accidents, such as uncontrolled material release or unsafe conditions leading to fire/explosion.
A fault in the malware caused the plant to shut down before any damage occurred. No explosion happened.
But the message was clear. Attackers had reached the last line of defence.
From a risk point of view, a near miss is still a serious warning. It may reflect strong safety design—or simple luck.
Rare Events, Severe Consequences
Confirmed cases of cyber attacks causing physical damage are still uncommon.
Over several decades, only a small number of such incidents have been publicly reported.
However, this can give a false sense of security.
Many events are never disclosed due to commercial or regulatory concerns. In addition, OT systems often lack detailed monitoring, so incidents may go undetected or misattributed as a systems malfunction.
At the same time, industrial sites deal with high energy processes and hazardous materials. If something goes wrong, losses can escalate quickly.
A single major event could cost billions, including repairs, lost production, environmental clean-up and legal claims.
The Insurance Challenge
While awareness of OT cyber risk is growing, insurance has struggled to keep up.
Traditional policies were not designed for cyber-physical events. As a result, coverage often falls between two areas.
Property insurance usually covers physical damage, but many policies now exclude cyber-related causes.
Cyber insurance tends to focus on data breaches and IT disruption. It often excludes physical damage.
This creates a gap. If a cyber attack causes physical damage, it may not be covered by either policy.
For operators of critical infrastructure, this is a serious issue.
A single incident could lead to large losses that exceed cyber policy limits, while property insurers may reject the claim due to cyber exclusions. The risk owner pays the entire loss out of pocket.
When Cyber Stops the Physical World
Even without physical damage, cyber incidents can still have major effects.
The 2021 ransomware attack on Colonial Pipeline is a good example. The attack mainly affected IT systems, but the company shut down operations as a precaution.
Fuel supplies were disrupted across large parts of the United States.
This and hundreds of ransomware incidents each year shows how closely digital systems are linked to physical operations.
More broadly, many manufacturers have found that IT failures can stop production entirely. In modern industry, the link between IT and OT is often economic as much as technical.
Why Insurers Find OT Risk Difficult
There are several reasons why this risk is hard to assess.
First, there is limited data. There are not many well-documented cases to analyse.
Second, every industrial site is different. Processes, equipment and safety systems vary widely, including the rigor of their engineering, making standard models difficult.
Third, this risk sits across several fields: cyber security, engineering, safety and finance. Each uses its own language and approach.
This can make it hard for insurers and operators to fully understand each other.
Closing the Gap
Addressing this issue will require closer collaboration.
One approach is to use more quantitative risk models (in this context, risk is $$). Instead of relying only on checklists or broad assessments, these models estimate the financial impact of specific cyber scenarios.
This helps organisations understand where to invest in security. It also helps insurers assess potential losses more clearly.
An Honest Way Forward
The truth is, this is still an evolving area.
Cyber-physical incidents are rare, and data is limited. No single group—operators, insurers or security experts—has all the answers.
What is clear is that cyber risk is no longer just digital. As systems become more connected, attacks will increasingly affect the physical world.
Dealing with this challenge will require engineers, cyber specialists, insurers and policymakers to work more closely together.
The aim is not only to prevent attacks, but also to understand and manage the financial impact when they happen.
Only by bridging the gap between cyber security, engineering and insurance can critical infrastructure remain resilient in a connected world.
By Neil Arklie, Cyber Insurance Expert, DeNexus
DeNexus has combed through 40 years of cybersecurity incidents and have discovered only ~8 that have led to physical property damage due to malicious actors (e.g., Stuxnet). Consider there are thousands facilities globally and hundreds of ransomware driven incidents annually, but on a tiny fraction in 40 years have actually gone beyond downtime, to incur physical damage (e.g., equipment damage, explosion, fire, flooding). Meanwhile, property insurance policies exclude damage triggered by cyber events, and cyber insurance policies exclude property damage. There is a gap where cyber-induced physical damage is not a covered peril for the majority of industry.

Next-generation geospatial models to support coastal risk insurance and risk mitigation

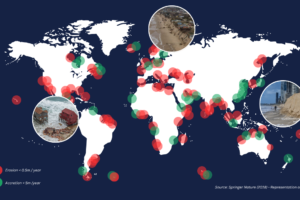
Coastal risks such as storm surges, erosion and the impacts of rising sea levels are escalating, impacting millions of homes and high-value assets. At the same time, the combination of this potential high impact with unpredictability is leaving some areas uninsurable. With the support of ESA's Business Applications and Space Solutions (BASS), UK-based Ocean Ledger has developed as a solution a next-generation coastal surge model to improve accuracy, transparency, and nuance for insurance risk exposure management.
Digital Elevation Models (DEMs) are essential for understanding and managing coastal risks. Existing models are however often static, may rely on outdated bathymetric or shoreline elevation data or are too coarse to capture localised coastal dynamics, which limits their value for risk assessment and operational decision-making.
Ocean Ledger is addressing the gaps in coastal risk data used in DEMs by integrating multiple sources of satellite Earth observation data, delivering a market-ready geospatial service that provides high-value insights for the insurance and climate resilience sectors, while supporting broader economic and societal protection against climate-driven hazards.
“The specific problem being addressed by Ocean Ledger is the absence of frequently updated, spatially granular and environmentally realistic elevation models which are suitable for integration into risk and insurance models,” explained Ocean Ledger CEO Paige Roepers.
In contrast to existing models, Ocean Ledger takes an observation-driven approach, effectively creating a digital twin of the coastline by using standardised satellite-derived topography workflows for shoreline elevation, shoreline position, vegetation and bathymetry. Their hazard model can be used in comparison to other models and to inform risk reduction strategies for those that own and operate assets.
“Through our project with ESA’s Business Applications and Space Solutions (BASS) team, we have been improving our DEMs, making them more accurate with the latest coastline elevation data and historical trend analysis. This allows us to make better predictions and offer more up-to-date insights than others,” says Ms Roepers. “With that, we can provide more transparency to make confident decisions around risk selection and pricing in highly exposed areas.”
Reflecting on the value of taking part in an ESA BASS programme, Ms Roepers added: “Working with ESA BASS has been a catalyst for us, significantly accelerating both our technological road map and commercial traction. The funding has allowed us to transition from high-level research and development to actionable market entry.”
“Having the ESA brand and funding behind us has been an invaluable asset and has helped us achieve the letters of support we needed to carry out pilots. We are looking forward to hopefully start a Demonstration Project with ESA BASS soon, to continue our journey with ESA and to deliver those pilots that will then take us closer to commercial contracts across Europe and the US.”
ESA BASS Applications and Partnerships Officer Ana Raposo said: “It has been wonderful to support Ocean Ledger and see the opportunities they have been able to secure within the ESA BASS Kick-start framework. I look forward to seeing how their journey continues and they go on to capitalise on the springboard for success they have now built.”

Supply Chain Compromises Impact Nx Console and GitHub Repositories

CISA is prioritizing the response to multiple emerging software supply chain intrusion campaigns targeting developer ecosystems Continuous Integration/Continuous Development (CI/CD) pipelines. These recent incidents, including the GitHub compromise via a malicious Nx Console Visual Studio Code (VS Code) extension and the “Megalodon” supply chain intrusion campaign, demonstrate how cyber threat actors are abusing tools and processes that support enterprise, cloud, and DevOps environments—specifically CI/CD pipelines, code extensions and workflows.
Threat actors leveraged a prior compromise of Nx developer systems to compromise a GitHub employee’s device through a poisoned third-party VS Code extension, resulting in unauthorized access and exfiltration of internal GitHub repositories. The malicious extension version (18.95.0) was distributed through VS Code’s automatic update mechanism, meaning systems with Nx Console previously installed may have received the malicious build without developers taking any manual installation action. GitHub released a security advisory on this activity, and CVE-2026-48027 has been assigned to the malicious version of Nx Console and added to CISA’s Known Exploited Vulnerabilities (KEV) Catalog.
Additionally, in a campaign known as “Megalodon,” a cyber threat actor injected malicious GitHub Action workflows to harvest CI/CD secrets, cloud credentials, and tokens, impacting both development and deployment pipelines in public GitHub repositories.
CISA urges organizations to implement the following recommendations to detect and remediate a potential compromise:
- Monitor and audit workflow files and contributor activity for suspicious pull requests and direct commits, particularly those authored by automated accounts.
- Revert unauthorized changes, especially from automated accounts, e.g., build-bot, auto-ci, ci-bot, pipeline-bot and especially those made after May 18, 2026.
If your organization discovers a compromise resulting from previously compromised GitHub or Nx Console software, CISA recommends the following steps:
- Conduct a forensics review of CI/CD logs, cloud audit trails, and affected developer machines.
- Rotate/revoke all secrets including: all credentials, tokens, and secrets accessible to CI/CD pipelines, including API keys, cloud provider credentials (Amazon Web Services, Google Cloud Platform, Microsoft Azure), SSH keys, Docker/npm/PyPI/Vault/Terraform/Kubernetes tokens, GitHub/GitLab/Bitbucket tokens, and developer or pipeline secrets.
- Notify proper stakeholders if necessary.
CISA recommends the following best practices for using package repos:
- Wait at least three hours before pulling a new package. This gives the software community time to identify suspicious or malicious packages before they are widely downloaded.
- Pin software to specific trusted versions. Pinning software prevents pulling a malicious or unscreened package during the build process.
- Only pull packages from known and trusted sources. Relying on known and trusted sources reduces the likelihood of downloading a package that has been maliciously forked.

Rethinking Critical Infrastructure Protection: From Static Defense to Adaptive Resilience

The End of Predictability
Critical infrastructure is no longer operating in a predictable, linear environment. For decades, the global approach to infrastructure protection was built on a foundational assumption of stability: threats were generally discrete, identifiable, and could be kept at bay through robust perimeter defenses. We built higher walls, thicker firewalls, and more rigid compliance frameworks. Today, however, these systems face overlapping disruptions driven by the convergence of climate pressures, sophisticated cyber-physical threats, and the exponentially increasing interdependencies between sectors.
The events of recent years have shattered the illusion of isolated failures. The global IT outage in mid-2024, triggered by a routine software update from a major cybersecurity vendor, demonstrated with chilling clarity how a single point of failure in the digital supply chain could cascade instantaneously across aviation, healthcare, finance, and logistics worldwide. Similarly, the increasing frequency of extreme weather events intersecting with targeted cyber-attacks on energy grids has shown that risks are no longer isolated. They are connected, dynamic, and often simultaneous.
Traditional protection models were explicitly built to defend against known threats. They focus heavily on prevention, hardening of assets, and reactive response protocols. While these elements remain essential components of a comprehensive security posture, they are no longer sufficient on their own. The current risk landscape requires a fundamental paradigm shift—a transition that allows critical infrastructure to continue functioning even when disruptions inevitably bypass defensive perimeters.
This is where the concept of resilience becomes not just an academic theory, but an operational imperative. Resilience is not merely about stopping disruptions; it is about maintaining core operations despite them. It reflects a strategic shift from static defense toward adaptive performance. Instead of asking exclusively, ‘How can we prevent failure?’, the governing question for modern security leaders must become: ‘How can our systems continue to operate, adapt, and deliver value under extreme stress?’
The Structural Limitations of Traditional Approaches
To understand why a new paradigm is necessary, we must critically examine the limitations of the traditional Critical Infrastructure Protection (CIP) models that still dominate national strategies.
One of the most significant vulnerabilities of traditional approaches is their entrenched reliance on sector-based, siloed thinking. Historically, energy, transport, water, telecommunications, and financial services have been managed, regulated, and secured as separate entities. However, modern infrastructure does not respect these artificial administrative boundaries. A disruption in the power grid immediately cripples telecommunications, which in turn blinds the logistics and transport sectors, leading to supply chain paralysis. This siloed management creates severe coordination gaps and exponentially increases the risk of cascading failures. When security teams only have visibility into their specific sector, they are effectively flying blind to the systemic risks building up in the interconnected web.
Another critical limitation is the over-reliance on static risk assessments. In many organizations, risk assessments are treated as compliance exercises—documents updated annually or bi-annually based on historical data and known scenarios. These static models are structurally incapable of keeping pace with fast-evolving, asymmetric threats. They assume a static baseline that no longer exists. When a novel threat emerges—whether a zero-day exploit or an unprecedented climatic anomaly—static defense mechanisms are often paralyzed by the lack of a pre-defined playbook.
Furthermore, traditional models often equate security with rigidity. The assumption is that the more locked-down a system is, the more secure it is. However, in complex, interdependent networks, rigidity often leads to brittleness. When a rigid system is pushed beyond its design parameters, it does not bend; it breaks catastrophically. To address these systemic vulnerabilities, the global security community must move beyond the illusion of absolute protection and embrace a more practical, dynamic, and adaptive approach.
The Adaptive Resilience Paradigm: A Four-Capability Framework
Transitioning from static defense to adaptive resilience requires more than a change in terminology; it requires a fundamental restructuring of how infrastructure is designed, governed, and operated. A practical and practitioner-focused way to operationalize resilience is through a continuous cycle of four core capabilities: Anticipation, Absorption, Adaptation, and Recovery.
Unlike traditional linear response models (Prevent - Respond - Recover), this framework operates as a continuous, dynamic loop — as illustrated in Figure 1 below.
1. Anticipate: Beyond Threat Intelligence
Anticipation goes beyond traditional threat intelligence. It is the ability to identify emerging risks, systemic vulnerabilities, and potential cascading effects before they materialize into full-scale crises. This requires moving from historical data analysis to strategic foresight. In highly interconnected environments, anticipation means mapping the hidden dependencies between your systems and third-party vendors. It involves continuous horizon scanning, utilizing AI-driven predictive analytics, and understanding the ‘weak signals’ that precede a systemic shock. True anticipation means recognizing that the next major disruption will likely come from a vector you have not explicitly planned for.
2. Absorb: Designing for Graceful Degradation
Absorption is the capacity of a system to withstand a shock without experiencing total systemic collapse. In traditional models, systems are often binary: they are either fully operational or completely offline. An adaptive system is designed for ‘graceful degradation.’ This means that when a cyber-attack or physical disruption occurs, the system can isolate the damaged components and maintain essential, life-safety, or mission-critical functions, even at a reduced capacity. Absorption requires structural redundancy, decentralized architectures, and the deliberate engineering of ‘circuit breakers’ that prevent a localized failure from cascading across the entire network.
3. Adapt: Real-Time Operational Agility
Adaptation is the most critical differentiator between rigid defense and true resilience. Absorption buys the system time; Adaptation is what the system does with that time. It is the ability to modify operations, reallocate resources, and change decision-making structures in real-time as a crisis unfolds. When the operational environment changes drastically, static playbooks become obsolete. Adaptation requires empowered, decentralized leadership where frontline managers have the authority to make rapid decisions without waiting for top-down consensus. It also involves technical agility—such as the ability to dynamically reroute data traffic, switch to alternative energy sources, or utilize backup communication channels seamlessly.
4. Recover: Improving Future Performance
In traditional models, recovery means returning to the pre-crisis baseline—the status quo. In the Adaptive Resilience framework, returning to the baseline is considered a failure of learning. If a system recovers only to its previous state, it remains just as vulnerable to the next disruption. True recovery involves continuous learning and systemic evolution. It means analyzing the root causes of the disruption, identifying the friction points in the response, and integrating those lessons into the system’s architecture and governance. Recovery must result in measurably improved performance and enhanced resilience against future shocks.
Insights from the Gulf: The Microcosm of Interdependency
The necessity of this adaptive approach is nowhere more evident than in high-density, technology-driven environments such as the Gulf region. Cities like Dubai and Abu Dhabi represent the vanguard of integrated urban environments, where the concept of the ‘Smart City’ has been fully realized. In these environments, critical infrastructure—water desalination, district cooling, automated transport, and digital governance—is hyper-connected through the Internet of Things (IoT) and centralized data hubs.
These regions serve as a critical microcosm for the future of global infrastructure. They highlight a crucial reality: resilience cannot be bolted on as an afterthought or activated only during a crisis; it must be built into the DNA of everyday operations. Systems that perform well under stress in these environments are those that are continuously monitored, regularly stress-tested through advanced simulations, and supported by robust, cross-sector governance frameworks.
A key insight from these hyper-connected environments is the critical importance of decision-making speed. In interdependent systems, the window for intervention is drastically compressed. A disruption in a smart grid can escalate into a multi-sector crisis in minutes, not hours. Delayed responses exponentially increase the likelihood of cascading failures. Therefore, real-time coordination, automated information sharing between public and private entities, and joint operational command centers are not optional luxuries—they are baseline requirements for survival.
Moreover, the Gulf region’s experience with large-scale events—such as Expo 2020 Dubai, which brought together 192 nations across a hyper-connected physical and digital platform—provides a powerful case study in operationalized resilience. Security planners were required to protect an environment where cyber threats, physical security, health emergencies, and logistical disruptions could materialize simultaneously and at scale. The approach adopted was not one of absolute prevention, but of continuous anticipation and rapid adaptation. Dedicated cross-agency coordination centers operated around the clock, empowered to make real-time decisions across sector boundaries. The lesson was unambiguous: resilience is a governance model, not merely a technical solution. It demands that human systems—command structures, communication protocols, and leadership cultures—evolve in parallel with the technical infrastructure they are designed to protect. This is a lesson that applies equally to every infrastructure operator, regardless of geography or sector.
Actionable Recommendations for Security Leaders
For professionals, site managers, and policymakers working in critical infrastructure, transitioning to this adaptive model requires deliberate, sustained effort. The following practical actions can significantly strengthen institutional resilience without requiring an immediate, ground-up redesign of existing systems:
1. Map Cross-Sector Interdependencies: Move beyond internal risk assessments. Conduct rigorous mapping of your dependencies on external sectors (power, water, telecom, third-party IT vendors) to understand exactly how external failures will cascade into your operations.
2. Establish Real-Time Coordination Mechanisms: Break down the silos. Create joint communication protocols and shared dashboards between infrastructure operators, government agencies, and emergency responders to drastically reduce the time between detection and response.
3. Integrate Scenario-Based Planning: Abandon static risk matrices. Implement dynamic, scenario-based wargaming that simulates complex, multi-hazard environments (e.g., a simultaneous cyber-attack during an extreme weather event) to test the limits of your absorption and adaptation capabilities.
4. Design for Operational Flexibility: Engineer systems with the capacity for graceful degradation. Ensure that critical functions can be manually overridden or physically isolated from the broader network to maintain partial functionality under extreme stress.
5. Invest in Leadership Readiness: Resilience is ultimately a human endeavor. Train leaders to make high-stakes decisions under conditions of extreme uncertainty and incomplete information. Empower frontline managers to adapt protocols dynamically when rigid playbooks fail.
6. Embed Continuous Learning: Institutionalize the recovery phase. Create formal mechanisms to systematically extract lessons from every disruption, near-miss, and simulation, ensuring these insights are immediately integrated into future architectural and governance planning.
It is important to emphasize that these six actions are not isolated technical upgrades. They represent a coherent governance philosophy. Individually, each action strengthens a specific vulnerability.
Collectively, they create a self-reinforcing cycle of institutional resilience. Organizations that have begun this transition report not only a measurable improvement in their crisis response capabilities, but also greater confidence among leadership in navigating uncertainty. In an era defined by permanent volatility, the ability to adapt is no longer a competitive advantage—it is the baseline requirement for continued operational relevance.
Conclusion: The New Foundation of Governance
The future of critical infrastructure protection will not be defined by who can build the strongest defenses, but by who can sustain operations through the most severe disruptions. The illusion that we can predict and prevent every threat has been definitively shattered by the complex realities of the modern, interconnected world.
Transitioning from static defense to adaptive resilience is no longer a theoretical debate; it is the new foundation for effective infrastructure governance. By embracing a continuous cycle of anticipation, absorption, adaptation, and evolutionary recovery, security leaders can ensure that our most vital systems remain functional, reliable, and capable of supporting society—no matter what shocks the future holds.
Resilience is no longer an option. It is the definitive metric of survival.
About the Author
Prof. Ehab ElHegawy is Professor of Security Sciences and Head of Security Crisis Management at Dubai Police Academy, UAE, with 30 years of operational and academic experience.
The latest issue of Critical Infrastructure Protection & Resilience News has arrived

Please find here your downloadable copy of the Spring 2026 issue of Critical Infrastructure Protection & Resilience News, the official magazine of the International Association of CIP Professionals (IACIPP), for the latest views, features and news, including a Review of the recent Critical Infrastructure Protection & Resilience North America conference, held in Baton Rouge, Louisiana.
Critical Infrastructure Protection & Resilience News in this issue:
- Rethinking Critical Infrastructure Protection: From Static Defense to Adaptive Resilience
- When Cyber Attacks Reach the Physical World: The Growing Insurance Gap in Critical Infrastructure
- Interdependencies - The hidden links between heat, water, and energy
- Why Critical Infrastructure Should Use Drone Vulnerability Risk Assessments Now
- Detection vs. Deterrence: What Actually Stops Intruders
- Algorithmic Amplification Is Now a Critical Infrastructure Risk
- The Unblinking Eye: Advancing Critical Infrastructure Security through GDPR Friendly Iris Recognition
- Review of Critical Infrastructure Protection & Resilience North America
- Agency News
- Industry News
#criticalinfrastructureprotection #criticalinfrastructure #resilience #cybersecurity #emergencymanagement #riskmitigation #portsecurity #homelandsecurity #firstresponder #riskmanagement #ai #artificalintelligence #energysecurity #gridresilience

CISA, NCSC-UK and Partners Release Cybersecurity Advisory on Chinese Government-Linked Covert Networks

CISA and the United Kingdom’s National Cyber Security Centre, in collaboration with other federal and international partners, have released a cybersecurity advisory, Defending Against China-nexus Covert Networks of Compromised Devices, providing network defenders with vital tools and resources to combat the threat posed by Chinese government-linked threat actors’ use of covert networks of compromised devices.
The advisory outlines tactics, techniques, and procedures associated with Chinese government-linked covert networks built from compromised small-office-home-office routers, Internet of Things, and smart devices. It explains how threat actors leveraging these covert networks, including those previously tied to groups such as Volt Typhoon and Flax Typhoon, use large scale botnet infrastructure to obscure attribution and enable reconnaissance, intrusion, command-and-control, and data exfiltration.
The advisory provides tailored defensive guidance for cyber defenders to identify, baseline, and mitigate activity originating from dynamic, deniable covert networks to reduce the risk of organizational compromise.
CISA and partners recommend the following steps to protect against this threat:
• Map and understand network edge devices, developing a clear understanding of organizational assets and what should be connected to them.
• Baseline normal connections, especially to corporate VPNs or other similar devices.
• Maintain log collection and storage solutions to assist with detecting and responding to unauthorized access attempts.
• Implement multifactor authentication for remote connections.
For more information on Chinese government-linked threat actor activity, please visit CISA's China Threat Overview and Advisories page.

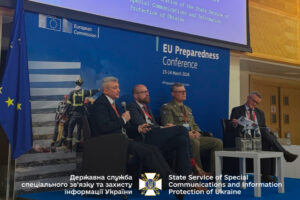
Ukraine's experience in critical infrastructure protection is increasingly shaping European thinking on resilience and preparedness

As part of the celebration of the first anniversary of the presentation of the EU Preparedness Union Strategy by the European Union, an EU conference on emergency preparedness, organized by the EU in Emergencies initiative, was held in Brussels (Kingdom of Belgium). The event became a platform for discussing achievements during the year of implementation of the Preparedness Strategy, as well as for exchanging experiences and discussing future challenges.
Vasyl Ananyev, a specialist in the Department of Critical Infrastructure Protection of the State Special Communications Administration, spoke during a session of experts on civil-military cooperation about the role of critical infrastructure protection in ensuring Ukraine's resilience.
“Resilience must be implemented at all levels, and a culture of preparedness should be strengthened in all our societies. The discussion clearly demonstrated that Ukraine’s experience is not only about the resilience of our nation — it is increasingly shaping the European approach to preparedness and resilience,” the State Special Communications Service specialist concluded.
Vasyl Ananyev thanked EU in Emergencies for its continued support for Ukraine and the opportunity to present our country’s experience in protecting critical infrastructure in the face of full-scale war and continuous air strikes on civilian infrastructure.
The two-day conference in Brussels on the occasion of the first anniversary of the EU Preparedness Strategy brought together government representatives, civil protection experts, military, private sector leaders and partners from across Europe. The participants of the event paid special attention to the lessons learned from Russia's military aggression against Ukraine, and also summed up the annual results of the implementation of the Union's Readiness Strategy.
Recall that in March last year, the European Union presented the EU Readiness Strategy, which contains plans for preventing and responding to new threats and challenges in the world.
[source: Vasyl Ananyev, News OKI Defense]
1 2 3 4 5 69