New report explores use of robotics and unmanned systems in the fight against crime
Europol has published The Unmanned Future(s): The Impact of Robotics and Unmanned Systems on Law Enforcement. The report, produced by the Europol Innovation Lab, provides an in-depth analysis of how unmanned systems could change society, crime and law enforcement, and discusses the challenges and opportunities they present.
The report underscores the rapid advancement and integration of unmanned systems in various sectors, including law enforcement. As these technologies become more sophisticated and widespread, they offer new opportunities for law enforcement operations and operational support. However, they also introduce new security threats – such as misuse by criminal and terrorist groups – and regulatory challenges that law enforcement agencies must address to ensure public safety and maintain trust.
"The integration of unmanned systems into crime is already here, and we have to ask ourselves how criminals and terrorists might use drones and robots some years from now. Just as the internet and smartphones presented significant opportunities as well as challenges, so will this technology. Our new report by Europol’s Innovation Lab explores the future operating environment for European law enforcement agencies and suggests actions needed today in order to effectively combat crime while upholding public trust and fundamental rights tomorrow." said Catherine De Bolle,Europol Executive Director.
One chapter of the report highlights the role of war as a driver for innovation in unmanned systems. Recent conflicts, such as the ongoing Russian war of aggression against Ukraine, have accelerated the development and deployment of advanced unmanned systems. The lessons learnt from these conflicts are invaluable for law enforcement agencies in Europe as they prepare for the future operating environment.
Some of the key topics covered in the report include:
Increasing use of unmanned systems
Unmanned systems are becoming increasingly useful, affordable and widely available, with applications in both public and private sectors. Law enforcement agencies across Europe are scaling up adoption of such systems, including drones and robots, to enhance situational awareness, improve safety and extend operational reach. These systems are employed for a range of tasks, such as monitoring, crime scene mapping, search and rescue operations, and the disposal of explosive ordnance, among others. Converging technologies present a significant opportunity for a breakthrough in the capabilities of unmanned systems.
Technical and regulatory challenges
The report highlights significant technical limitations and regulatory gaps that hinder the effective use of unmanned systems in law enforcement. Issues such as limited autonomy, dependence on industrial suppliers and the lack of clear guidelines for autonomous operations pose substantial challenges.
Security threats
Criminal and terrorist groups are rapidly adopting unmanned systems for illicit activities. The report warns of the potential for these systems to be used for criminal surveillance, smuggling and even attacks. The increasing accessibility and versatility of drones, in particular, present serious security concerns.
Public trust and regulation
Public trust is crucial for the legitimacy of law enforcement capabilities. The report emphasises the need for transparency, accountability and public engagement in the deployment of unmanned systems. Current regulations, while advancing, still have gaps, particularly in addressing non-compliant or criminal use.
Future operating environment
The future of law enforcement will require policing in a three-dimensional space, as unmanned systems operate in the air and on the ground, as well as on and under water. This shift will necessitate new strategies, technologies and training for law enforcement agencies.
Recommendations
The report provides a set of recommendations for European law enforcement agencies, including the development of a strategic direction, the establishment of a competency hub and the integration of unmanned systems into existing information systems. It also calls for investments in training, education and public trust-building initiatives.
The report is available for download on the Europol website and includes detailed insights, case studies and recommendations for law enforcement agencies, policymakers and other stakeholders.
CISA Unveils Enhanced Cross-Sector Cybersecurity Performance Goals

New Benchmarks Empower Organizations to Counter Emerging Threats, Build Cyber Resilience, and Strengthen Governance
the Cybersecurity and Infrastructure Security Agency (CISA) released version 2.0 of its Cross-Sector Cybersecurity Performance Goals (CPGs), offering organizations a more robust framework for integrating cybersecurity into daily operations. The updated CPGs align with the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) 2.0, incorporates three years of operational insights, and address emerging threats through data-driven, actionable guidance. These enhancements are designed to promote accountability, improve risk management, and support strategic cybersecurity governance across sectors.
The Cross-Sector CPGs represent a targeted subset of best practices, carefully selected through extensive consultation with industry leaders, government stakeholders, and cybersecurity experts. Designed to meaningfully reduce risks to critical infrastructure and safeguard the American public, these goals offer a practical starting point for small and medium-sized organizations. By focusing on a limited set of high-impact actions, the CPGs help prioritize cybersecurity investments that deliver measurable improvements in resilience and risk reduction.
The updated goals offer expanded and clarified guidance across key cybersecurity domains—including account and device security, data protection, governance, vulnerability management, supply chain risk, and incident response and recovery. Building on the foundation of version 1.0.1, CPG 2.0 introduces several notable improvements:
- Governance Emphasis: A new “Govern” function underscores the critical role of organizational leadership in cybersecurity, regrouping existing goals and introducing two new ones focused on risk management strategy, policy development, and executive accountability.
- Unified Goal Structure: Operational Technology (OT) and Information Technology (IT) goals are now consolidated into universal goals, eliminating silos across IT, Internet of Things (IoT), and OT environments.
- Threat-Responsive Expansion: New goals address emerging threats, third-party risk, zero trust architecture, and incident communication protocols.
- Streamlined Framework: Redundant, unclear, or underutilized goals have been removed to improve clarity and usability.
- Enhanced Documentation: Each goal now includes clearer methodology and supporting materials to reduce guesswork and improve implementation.
“Over the past year, CISA has engaged extensively with hundreds of stakeholders across both the public and private sectors to ensure the updated goals reflect real-world challenges and operational realities,” said Madhu Gottumukkala, Acting CISA Director. “Version 2.0 demonstrates our commitment to listening to and incorporating partner feedback to deliver practical, outcome-driven guidance that organizations can act on. These goals are applicable across all critical infrastructure sectors and offer foundational protection for organizations regardless of their cybersecurity maturity. We encourage all organizations to adopt the new CPGs and continue sharing feedback to help us refine future iterations.”
The Cross-Sector CPGs serve three primary purposes:
- Provide measurable actions that critical infrastructure entities can take to achieve a basic level of cybersecurity.
- Bridge communication gaps between IT/OT technical staff and organizational leadership to align on cybersecurity priorities.
- Support strategic planning by offering clear guidance that informs both near- and long-term cybersecurity investments.
CISA encourages organizations to adopt the voluntary Cross-Sector CPGs. To learn more about the updated Cybersecurity Performance Goals and how they can support your organization’s cybersecurity program, visit Cross-Sector Cybersecurity Performance Goals and Objectives.

CISA Releases Dynamic New Guide for Stadium and Arena Owners to Fortify Operations, Mitigate Vulnerabilities and Elevate Emergency Preparedness

The Cybersecurity and Infrastructure Security Agency (CISA) released the Venue Guide for Mitigating Dependency Disruptions, a new resource designed to strengthen the resilience of public gathering venues. This guide provides stadium and arena owners and operators with baseline strategies to mitigate the consequences of potential disruptions to four critical lifeline sectors—including Energy, Water and Wastewater Systems, Communications, and Transportation.
CISA developed this guide in close collaboration with government and industry experts from the four lifeline sectors as a concise, actionable resource for stadium and arena owners. Tailored for major public gathering events- such as FIFA World Cup 2026, America 250, and 2028 Summer Olympics, the guide draws on lessons learned from recent disruptions at high-profile public gathering sports and entertainment facilities across the United States and internationally. It equips critical infrastructure stakeholders with a clear understanding of threats to lifeline sectors and provides effective strategies to safeguard operations, reduce vulnerabilities, and enhance preparedness.
“Today’s risk environment is rapidly evolving, posing serious threats and disruptions to U.S. critical infrastructure and public gathering venues,” said CISA Acting Director Madhu Gottumukkala. “CISA is committed to working hand-in-hand with our government and industry partners to deliver actionable guidance that helps mitigate these risks. This guide empowers venue owners and operators to proactively assess vulnerabilities tied to dependent lifeline services and integrate those insights into contingency planning—ultimately reducing potential consequences and strengthening operational resilience.”
The Venue Guide for Mitigating Dependency Disruptions aligns with Executive Order 14234 Establishing the White House Task Force on the World Cup 2026, Executive Order 14239 Achieving Efficiency through State and Local Preparedness, and Executive Order 14328 Establishing the White House Task Force on the 2028 Summer Olympics. This guide assists critical infrastructure and public venue owners and operations with:
- Understanding the lifeline sector dependencies and interdependencies that their venues may rely on;
- Assessing security risks and associated key components of a facility evaluation; and
- Focusing on continued information-sharing and relationship-building with key partners such as local services providers, first responders, and CISA Security Advisors.
“Robust partnerships are essential to safeguarding critical infrastructure and public gatherings. By sharing threat intelligence, risk mitigation strategies, and other vital information, we strengthen our collective ability to anticipate and respond to potential disruptions. CISA’s newly released guide empowers venue owners and operators to assess dependencies and implement targeted mitigation strategies,” said CISA Executive Assistant Director for Infrastructure Security Steve Casapulla. “We deeply value the insights and collaboration from our government and industry partners across four lifeline sectors, which were instrumental in shaping this timely and practical resource. CISA urges all organizations that host events to review the guide and take proactive steps to enhance infrastructure security and resilience.”

Mistaking AI vulnerability could lead to large-scale breaches, NCSC warns

NCSC raises alert on “dangerous” misunderstanding of emergent class of vulnerability in generative artificial intelligence (AI) applications.
The National Cyber Security Centre (NCSC) – a part of GCHQ – has shared critical insights cautioning cyber security professionals against comparing prompt injection and more classical application vulnerabilities classed as SQL injection.
A new blog advises that, contrary to first impressions, prompt injection attacks against generative artificial intelligence applications may never be totally mitigated in the way SQL injection attacks can be.
Unlike SQL mitigation techniques, which hinge on enforcing a clear separation between data and instructions, prompt injection exploits the inability of large language models (LLMs) to distinguish between the two.
Without action addressing this misconception, the NCSC warns, websites risk falling victim to data breaches exceeding those seen from SQL injection attacks in the 2010s, impacting UK businesses and citizens into the next decade.
Backing proactive adoption of cyber risk management standards, the NCSC challenges claims that prompt injections can be ‘stopped’.
Instead, it suggests efforts should turn to reducing the risk and impact of prompt injection and driving up resilience across AI supply chains.
As AI technologies become embedded in more UK business operations, the NCSC calls on AI system designers, builders and operators to take control of manageable variables, acknowledging that LLM systems are “inherently confusable” and their risks managed in different ways.

Disaster Assistance High-Risk Series: State and Local Response Capabilities

GAO was asked to review long-standing challenges and emerging issues in federal response efforts for recent disasters, including Hurricanes Helene and Milton, the 2025 Los Angeles wildfires, and the July 2025 Texas floods. In September 2025, GAO issued the first report in a series on disaster response, focusing on the federal response workforce. This second report in the series provides information on federal disaster preparedness and response assistance provided before and during recent disasters, variation in state and local response capabilities, and considerations for potential changes to disaster response roles.
Preparing for and responding to disasters, like hurricanes and wildfires, begins with state and local governments. But, their ability to do so varies widely. The federal government provides extensive support through grants, training, and other assistance.
In light of recent interest in reviewing the federal role in disaster response, federal and state officials told us what they would want policymakers to consider with any potential changes. This includes clear communication, time to prepare, and FEMA's federal coordination role.
This is the second report in a series on disaster response. The first was on the federal response workforce.
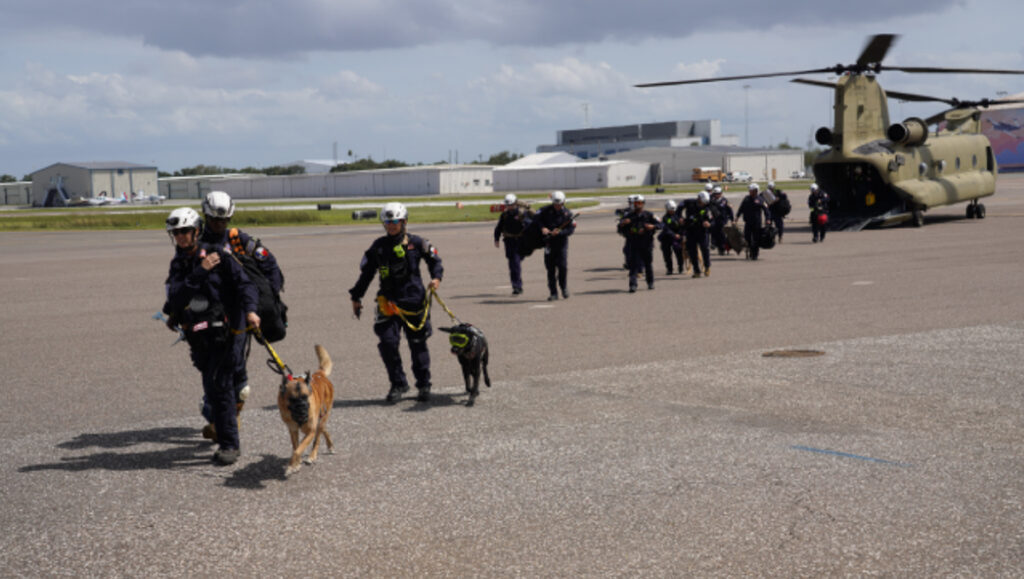
State Response Team Assisting after Hurricane Helene
All levels of government have a role in preparing for and responding to disasters, with the Federal Emergency Management Agency (FEMA) leading the federal response. It has been nearly 20 years since the Post-Katrina Emergency Management Reform Act of 2006 required actions—such as the development of a national preparedness system—to address shortcomings in the nation’s disaster response system. Federal, state, and local governments, however, continue to face challenges preparing for and responding to large-scale disasters. Recent disasters, such as Hurricanes Helene and Milton in 2024, the Los Angeles wildfires in early 2025, and the July 2025 flooding in Texas, demonstrate the need for government-wide action to deliver assistance effectively.
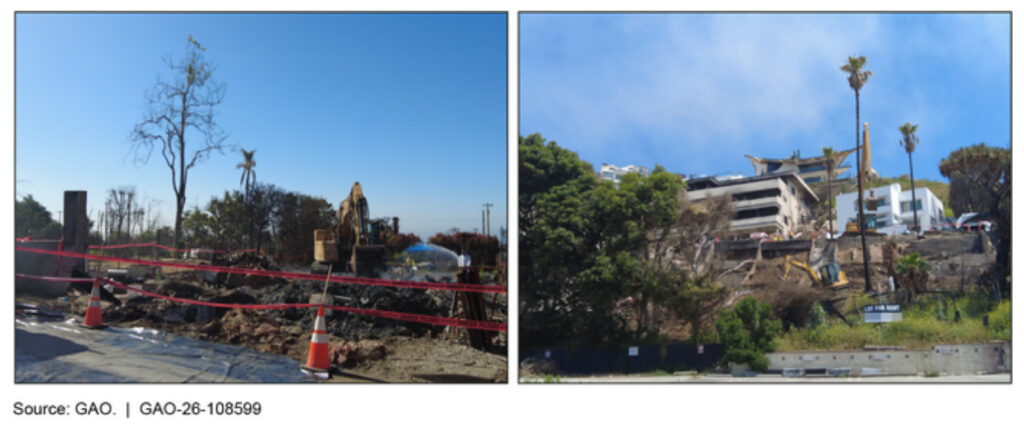
The federal government provides extensive support to state and local governments for disaster preparedness and response. For example, FEMA provides preparedness grants, training, and technical support to strengthen state and local emergency management capabilities. FEMA and other federal agencies, such as the U.S. Army Corps of Engineers and the Environmental Protection Agency, also supplement state and local efforts during disaster response (see figure).
U.S. Army Corps of Engineers Debris Removal Efforts After 2025 Los Angeles Wildfires
GAO analyzed selected states’ assessments of their disaster response capabilities and found that capability levels varied widely. Federal, state, and local officials GAO interviewed also emphasized the variation in capabilities at the state and local level—including challenges for rural or less resourced jurisdictions, even if they are within a well-resourced state.
GAO has previously reported on challenges with FEMA and other federal agencies’ disaster assistance and added Improving the Delivery of Disaster Assistance to GAO’s High-Risk list in February 2025 to highlight the recommendations GAO has made to improve federal disaster efforts.
Congress and the President have signaled an interest in reforms to FEMA. For example, the President signed Executive Orders in January and March 2025, respectively, establishing a FEMA Review Council to recommend improvements to FEMA and requiring review and revision of response and preparedness policies. Broader reform of FEMA’s mission, structure, or operations may address long-standing challenges with federal disaster efforts. Given the current levels of federal support and wide variation in state and local response capabilities, officials at the federal and state levels provided the following considerations for policymakers for communicating and implementing any such changes:
- Clear communication and guidance. States raised concerns about the uncertainty of the future of FEMA’s role. For example, state officials said it is challenging to plan in the absence of clear, consistent, and accurate guidance and emphasized the importance of consistent messaging about any changes, including technical assistance and training. GAO’s work following Hurricane Katrina also emphasized the importance of communicating clear roles and responsibilities.
- Time to prepare. Given that state and local governments rely on significant federal disaster support, federal and state officials emphasized the need for adequate time for these entities to prepare for any changes in disaster response roles.
- Catastrophic or widespread disasters. Federal officials underscored that there will always be catastrophic disasters for which even the most well-equipped states would require some level of federal financial or other support.
- Federal-level coordination. FEMA also plays a vital role as the coordinating agency for the federal response to disasters. For example, FEMA has the statutory authority to assign other federal agencies to perform disaster response tasks that those agencies might not otherwise have authority to perform.
GAO analyzed information from interviews conducted with federal agencies involved in disaster response and state and local governments impacted by disasters in recent years. Additionally, GAO analyzed preparedness assessments for the 10 states that received major disaster declarations for these recent disasters. To provide information on preparedness and response assistance, we summarized data on FEMA’s obligations for these disasters and amounts awarded through selected FEMA preparedness grants.

Terrorist Watchlist: FBI Should Improve Outreach Efforts to Nonfederal Users

The Threat Screening Center, administered by FBI, is responsible for managing the terrorist watchlist. In recent years, Members of Congress have raised questions about how nonfederal entities use the terrorist watchlist.
GAO was asked to examine the use of the terrorist watchlist by nonfederal law enforcement entities. This report examines (1) nonfederal entities’ reporting of terrorist watchlist encounters to FBI and opportunities for improvement and (2) steps FBI has taken to ensure nonfederal entities’ awareness of watchlist policies through outreach and state-led trainings.
When state and local law enforcement officers encounter people—e.g., in traffic stops—officers check their names against state database systems. The systems will return an alert if a name potentially matches one on the terrorist watchlist, which is managed by the FBI.
In half the interviews with law enforcement agencies, officials said their officers may not always know how to properly respond to these alerts.
We recommended that the FBI develop a communications plan to tell law enforcement agencies about the policies around the terrorist watchlist, and a process to review states' training on the policies.
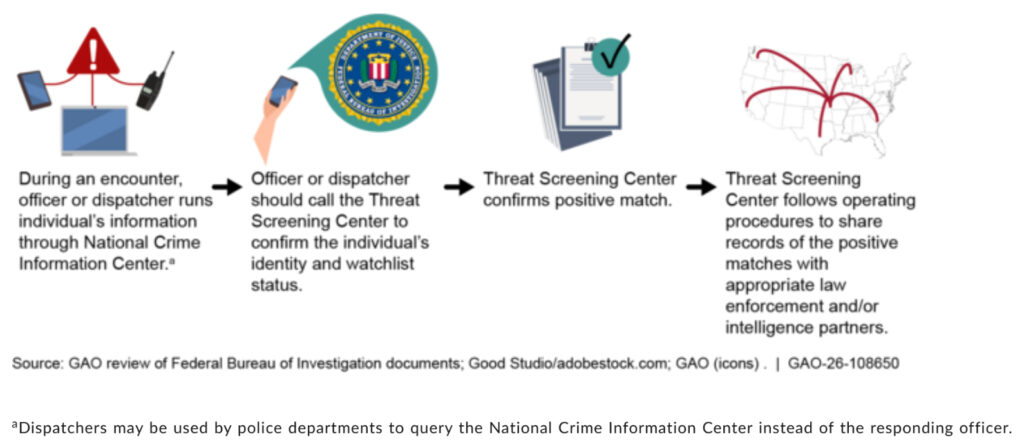
Nonfederal law enforcement officers query encountered individuals against the terrorist watchlist during routine police interactions, such as traffic stops. After encountering a potentially terrorist watchlisted individual, nonfederal law enforcement officers receive instructions, via the National Crime Information Center (NCIC), to contact the Federal Bureau of Investigation’s (FBI) Threat Screening Center to determine whether the individual is a positive or negative match to the terrorist watchlist.
GAO found that almost half of the law enforcement entities GAO interviewed in four states (12 of 26 entities, including police and sheriff’s departments) reported that officers were not consistently reporting encounters with potentially terrorist watchlisted individuals in instances where it is warranted. Seeking information to understand the extent to which nonfederal law enforcement entities are consistently reporting terrorist watchlist encounters could improve the accuracy of watchlist records.
Nonfederal Law Enforcement Steps When Responding To Terrorist Watchlist Encounters
The Threat Screening Center uses outreach efforts to communicate terrorist watchlisting policies to nonfederal law enforcement entities that use the terrorist watchlist. However, GAO found that FBI has not ensured nonfederal law enforcement entities are aware of terrorist watchlist policies and has not taken steps to develop a communication plan for its outreach efforts. Developing a communication plan with goals and measures as well as periodic assessments of progress would help accomplish this. Additionally, FBI’s Criminal Justice Information Services does not ensure states train NCIC users on terrorist watchlist policies. Without developing a process to review states’ efforts to do so, FBI cannot ensure that state training programs instruct nonfederal law enforcement to properly protect and respond to terrorist watchlist information.
GAO reviewed watchlist policies and training resources for nonfederal entities and collected encounter data for fiscal years 2019 through 2024. GAO interviewed nonfederal law enforcement officials in four states selected based on the number of encounters and other factors. While not generalizable, these interviews provided insights into officials’ awareness of policies and training.
This is the public version of a sensitive report GAO issued in August 2025. Information on encounter data and official FBI instructions on handling watchlist encounters that FBI deemed sensitive has been omitted.
GAO recommends that FBI (1) seek information to understand the extent to which nonfederal law enforcement entities are consistently reporting terrorist watchlist encounters, (2) develop a communication plan to improve its outreach efforts, and (3) develop a process to review state efforts to instruct NCIC users about watchlist policies. FBI concurred with the recommendations.

CISA Launches New Platform to Strengthen Industry Engagement and Collaboration

The Cybersecurity and Infrastructure Security Agency (CISA) launched a new Industry Engagement Platform (IEP) designed to facilitate structured, two-way communication between the agency and companies developing innovative and security technologies. The IEP enables CISA to better understand emerging solutions across the technology ecosystem while giving industry a clear, transparent pathway to engage with the agency.
“With the launch of this new platform, we’re opening the door wider to innovation—giving industry a direct line to share the tools and technologies that can help CISA stay ahead of evolving threats,” said CISA Acting Director Madhu Gottumukkala. “The private sector drives innovation and this collaboration is essential to our national resilience.”
The IEP allows organizations – including industry, non-profits, academia, government partners at all and the research community – with a structured process to request conversations with CISA subject matter experts to describe new technologies and capabilities. These engagements give innovators the opportunity to present solutions that may strengthen our nation’s cyber and infrastructure security.
Through customizable technology profiles, the IEP helps connect organizations to the right CISA experts by capturing areas of expertise and specific topics organizations wish to discuss. Participants may also upload capability overviews for CISA to reference in market research and in understanding emerging technologies across sectors.
While participation in the IEP does not provide preferential consideration for future federal contracts, it serves as a key channel for CISA to gain insight into new capabilities and market trends that support mission needs.
CISA encourages organizations with new, emerging, or advanced technology solutions to visit the Industry Engagement Platform. Current areas of interest include:
- Information technology and security controls
- Data, analytics, storage, and data management
- Communications technologies
- Any emerging technologies that advance CISA’s mission, including post-quantum cryptography and other next-generation capabilities
“Strategic collaboration is essential to strengthening national security and resilience,” Gottumukkala added. “The IEP is one of the ways CISA is aligning innovation with mission needs to advance the defense of our nation’s cyber and critical infrastructure.”

2025 CWE Top 25 Most Dangerous Software Weaknesses

The Cybersecurity and Infrastructure Security Agency (CISA), in collaboration with the Homeland Security Systems Engineering and Development Institute (HSSEDI), operated by the MITRE Corporation, has released the 2025 Common Weakness Enumeration (CWE) Top 25 Most Dangerous Software Weaknesses. This annual list identifies the most critical weaknesses adversaries exploit to compromise systems, steal data, or disrupt services.
Prioritizing the weaknesses outlined in the Top 25 is integral to CISA’s Secure by Design and Secure by Demand initiatives, which promote building and procuring secure technology solutions. CISA and MITRE encourage organizations to review this list and use it to inform their respective software security strategies.
The 2025 CWE Top 25:
• Supports Vulnerability Reduction: By focusing on the Top 25, organizations can prioritize lifecycle changes, adopt safer architectural decisions, and reduce high-impact vulnerabilities related to injection, access control, and memory safety defects.
• Drives Cost Efficiencies: Eliminating weaknesses early reduces downstream remediation; addressing them before deployment is more efficient and cost effective than patching, reconfiguring, or responding to emergency incidents.
• Strengthens Customer and Stakeholder Trust: Transparent efforts to identify, mitigate, and monitor weaknesses demonstrate commitment to Secure by Design principles. Organizations that prioritize eliminating recurring weaknesses contribute to a safer software ecosystem.
• Promotes Consumer Awareness: The Top 25 empowers consumers to understand underlying causes of common vulnerabilities, supports more informed purchasing decisions, and encourages adoption of products that follow robust security engineering practices.
Recommendations for Stakeholders:
• For Developers and Product Teams: Review the 2025 CWE Top 25 to identify high-priority weaknesses and adopt Secure by Design practices in development.
• For Security Teams: Incorporate the Top 25 into vulnerability management and application security testing to assess and mitigate critical weaknesses.
• For Procurement and Risk Managers: Use the Top 25 as a benchmark when evaluating vendors and apply Secure by Demand guidelines to ensure investment in secure products.
By shining a light on the most dangerous software weaknesses, CISA and MITRE reinforce collective efforts to reduce vulnerabilities at the source, strengthen national cybersecurity, and improve long-term resilience.

CISA Update Cross-Sector Cybersecurity Performance Goals (CPG 2.0)

CISA has released an updated Cross-Sector Cybersecurity Performance Goals (CPG 2.0) with measurable actions for critical infrastructure owners and operators to achieve a foundational level of cybersecurity.
This update incorporates lessons learned, aligns with the most recent National Institute of Standards and Technology Cybersecurity Framework revisions, and addresses the most common and impactful threats facing critical infrastructure today.
CPG 2.0 includes a new component focused on the essential role of governance in managing cybersecurity. It emphasizes accountability, risk management, and strategic integration of cybersecurity into day-to-day operations, reinforcing the principle that effective governance is the cornerstone of a resilient cyber posture.
CPGs are streamlined and outcome-driven cybersecurity protections for information technology and operational technology environments and provide:
• Clear, foundational practices aligned with real-world threats.
• Straightforward, outcome-oriented language to aid implementation.
• A baseline for guiding investment, benchmarking progress, and reducing risk in measurable ways.
For more information, visit CPG 2.0 and Cross-Sector Cybersecurity Performance Goals | CISA

PRC State-Sponsored Actors Use BRICKSTORM Malware Across Public Sector and Information Technology Systems

The Cybersecurity and Infrastructure Security Agency (CISA) is aware of ongoing intrusions by People’s Republic of China (PRC) state-sponsored cyber actors using BRICKSTORM malware for long-term persistence on victim systems. BRICKSTORM is a sophisticated backdoor for VMware vSphere1,2 and Windows environments.3 Victim organizations are primarily in the Government Services and Facilities and Information Technology Sectors. BRICKSTORM enables cyber threat actors to maintain stealthy access and provides capabilities for initiation, persistence, and secure command and control. The malware employs advanced functionality, including multiple layers of encryption (e.g., HTTPS, WebSockets, and nested TLS), DNS-over-HTTPS (DoH) to conceal communications, and a SOCKS proxy to facilitate lateral movement and tunneling within victim networks. BRICKSTORM also incorporates long-term persistence mechanisms, such as a self-monitoring function that automatically reinstalls or restarts the malware if disrupted, ensuring its continued operation.
The initial access vector varies. In one confirmed compromise, PRC state-sponsored cyber actors accessed a web server inside the organization’s demilitarized zone (DMZ), moved laterally to an internal VMware vCenter server, then implanted BRICKSTORM malware. See CISA, the National Security Agency, and Canadian Cyber Security Centre’s (Cyber Centre’s) joint Malware Analysis Report (MAR) BRICKSTORM Backdoor for analysis of the BRICKSTORM sample CISA obtained during an incident response engagement for this victim. The MAR also discusses seven additional BRICKSTORM samples, which exhibit variations in functionality and capabilities, further highlighting the complexity and adaptability of this malware.
After obtaining access to victim systems, PRC state-sponsored cyber actors obtain and use legitimate credentials by performing system backups or capturing Active Directory database information to exfiltrate sensitive information. Cyber actors then target VMware vSphere platforms to steal cloned virtual machine (VM) snapshots for credential extraction and create hidden rogue VMs to evade detection.
CISA recommends that network defenders hunt for existing intrusions and mitigate further compromise by taking the following actions:
• Scan for BRICKSTORM using CISA-created YARA and Sigma rules; see joint MAR BRICKSTORM Backdoor.
• Block unauthorized DNS-over-HTTPS (DoH) providers and external DoH network traffic to reduce unmonitored communications.
• Take inventory of all network edge devices and monitor for any suspicious network connectivity originating from these devices.
• Ensure proper network segmentation that restricts network traffic from the DMZ to the internal network.
See joint MAR BRICKSTORM Backdoor for additional detection resources.
1 2 3 4 5 6 … 48