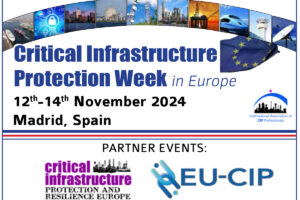
The International Association of Critical Infrastructure Protection Professionals (IACIPP) has announced the launch of ‘Critical Infrastructure Protection Week’ in Europe as part of an initiative focused towards enhancing collaboration and cooperation amongst the industry.
With the imminent implementation of The Critical Entities Resilience Directive (CER Directive), which lays down obligations on EU Member States to take specific measures to ensure that essential services and infrastructures, for the maintenance of vital societal functions or economic activities, are provided in an unobstructed manner in the internal market. The deadline of 17th October 2024 is set for when Member States shall adopt and publish the measures necessary to comply with this Directive.
The NIS2 Directive, also known as the Network and Information Security Directive, is also a significant piece of legislation being implemented by 17th October 2024, aimed at improving cyber security and protecting critical infrastructure across the European Union (EU).
It builds upon the previous NIS Directive, addressing its shortcomings and expanding its scope to enhance security requirements, reporting obligations, and crisis management capabilities.
Compliance with the CER Directive and NIS2 Directive are crucial for businesses operating in the EU to safeguard their systems, mitigate threats, and ensure resilience. Penalties are enforceable on agencies and operators for non-compliance.
In light of the forthcoming challenges with the Directives, and the ever increasing threats against European critical infrastructures, IACIPP is launching ‘CIP Week’ in Europe to help raise awareness and promote greater collaboration amongst operators, agencies and the CI security community.
John Donlon QPM, Chairman of The International Association of Critical Infrastructure Protection Professionals, said, “IACIPP is delighted to be announcing this new initiative in Europe, with the important aim of encouraging greater information sharing, collaboration and co-operation within the industry.”
“The CER and NIS2 Directives are two of the most important pieces of legislation to arrive in Europe in recent years, and IACIPP along with other professional bodies have a degree of concern over the lack of preparation of some of the operators and agencies for the October deadline, and believe more needs to be done to ensure these minimum standards are met, and indeed exceeded in subsequent years.”
“We are delighted the ‘Critical Infrastructure Protection & Resilience Europe’ conference and exhibition and ‘EU-CIP Horizon Europe Project’ conference are the first two events to contribute towards CIP Week, which we aim to be an annual event. Madrid is an excellent location for the launch of this program, with the CN-PIC driving Spain’s efforts to meet the Directives’ deadlines and be prepared.” Added Mr Donlon.
Critical Infrastructure Protection & Resilience Europe (CIPRE) is the premier conference in Europe to discuss the operational threats and challenges, delivering though leadership and strategies for operators and agencies to plan security and resilience to their operations and assets.
The EU-CIP Horizon Europe Project* is set up to establish a novel pan European knowledge network for Resilient Infrastructures, which will enable policy makers to shape and produce data-driven evidence-based policies, while boosting the innovation capacity of Critical Infrastructures (CI) operators, authorities, and innovators (including SMEs).
Emilia Gugliandolo, Project Coordinator of EU-CIP, said, “The EU-CIP Project is delighted to be invited as part of the CIP Week initiative, enabling greater opportunities for the industry to explore the challenges and opportunities for bringing about synergetic, emerging disruptive solutions to security issues via cross-projects collaboration and innovation. We look forward to successful collaborations between the sectors and professionals in achieving the overall goals for the industry.”
IACIPP is an international association of practitioners and professionals involved in the security, resilience and safety of critical infrastructure, both physical and information infrastructure, open to critical infrastructure operators and government agencies, including site managers, security officers, government agency officials, policy makers, research & academia. The Association also aims to share ideas, information, experiences, technology and best practise to enhance these objectives.
IACIPP is inviting the industry to join in CIP Week in Madrid on 12th-14th November 2024.