NSA Releases First in Series of Zero Trust Implementation Guidelines

The National Security Agency (NSA) is releasing the first two products in a series of Zero Trust Implementation Guidelines (ZIGs) to provide practical, actionable recommendations to facilitate the implementation of Zero Trust (ZT).
This series of reports outlines the steps to implement the technologies and processes that support achieving the Target-level ZT Capabilities, Activities, and Expected Outcomes described in the Department of War (DoW) CIO ZT Framework.
The Primer and Discovery Phase are the gateway to ZT implementation, providing guidance and direction to ensure organizations are fully equipped to digest and implement the Phase 1 and Phase 2 ZIGs upon their release.
The Primer outlines the strategy and principles used to develop the ZIGs and provides a holistic approach to maximizing the usage of the series. Notably, the ZIGs are designed to be modular, allowing organizations at different levels of ZT maturity to select and implement the capabilities most relevant to the needs of their environment.
The Discovery Phase is intended to help organizations establish foundational visibility and understand the critical data, applications, assets, and services, as well as access and authorization activity existing within the architecture. The goal of this initial phase is to enable informed prioritization and planning by creating a reliable baseline that supports effective ZT implementation.
System owners, cybersecurity professionals, and stakeholders should review these foundational guidelines to gain a deeper understanding of ZT activities and their organization’s operational landscape in preparation for the release of the Phase 1 and Phase 2 ZIGs.

New report explores use of robotics and unmanned systems in the fight against crime

Europol has published The Unmanned Future(s): The Impact of Robotics and Unmanned Systems on Law Enforcement. The report, produced by the Europol Innovation Lab, provides an in-depth analysis of how unmanned systems could change society, crime and law enforcement, and discusses the challenges and opportunities they present.
The report underscores the rapid advancement and integration of unmanned systems in various sectors, including law enforcement. As these technologies become more sophisticated and widespread, they offer new opportunities for law enforcement operations and operational support. However, they also introduce new security threats – such as misuse by criminal and terrorist groups – and regulatory challenges that law enforcement agencies must address to ensure public safety and maintain trust.
"The integration of unmanned systems into crime is already here, and we have to ask ourselves how criminals and terrorists might use drones and robots some years from now. Just as the internet and smartphones presented significant opportunities as well as challenges, so will this technology. Our new report by Europol’s Innovation Lab explores the future operating environment for European law enforcement agencies and suggests actions needed today in order to effectively combat crime while upholding public trust and fundamental rights tomorrow." said Catherine De Bolle,Europol Executive Director.
One chapter of the report highlights the role of war as a driver for innovation in unmanned systems. Recent conflicts, such as the ongoing Russian war of aggression against Ukraine, have accelerated the development and deployment of advanced unmanned systems. The lessons learnt from these conflicts are invaluable for law enforcement agencies in Europe as they prepare for the future operating environment.
Some of the key topics covered in the report include:
Increasing use of unmanned systems
Unmanned systems are becoming increasingly useful, affordable and widely available, with applications in both public and private sectors. Law enforcement agencies across Europe are scaling up adoption of such systems, including drones and robots, to enhance situational awareness, improve safety and extend operational reach. These systems are employed for a range of tasks, such as monitoring, crime scene mapping, search and rescue operations, and the disposal of explosive ordnance, among others. Converging technologies present a significant opportunity for a breakthrough in the capabilities of unmanned systems.
Technical and regulatory challenges
The report highlights significant technical limitations and regulatory gaps that hinder the effective use of unmanned systems in law enforcement. Issues such as limited autonomy, dependence on industrial suppliers and the lack of clear guidelines for autonomous operations pose substantial challenges.
Security threats
Criminal and terrorist groups are rapidly adopting unmanned systems for illicit activities. The report warns of the potential for these systems to be used for criminal surveillance, smuggling and even attacks. The increasing accessibility and versatility of drones, in particular, present serious security concerns.
Public trust and regulation
Public trust is crucial for the legitimacy of law enforcement capabilities. The report emphasises the need for transparency, accountability and public engagement in the deployment of unmanned systems. Current regulations, while advancing, still have gaps, particularly in addressing non-compliant or criminal use.
Future operating environment
The future of law enforcement will require policing in a three-dimensional space, as unmanned systems operate in the air and on the ground, as well as on and under water. This shift will necessitate new strategies, technologies and training for law enforcement agencies.
Recommendations
The report provides a set of recommendations for European law enforcement agencies, including the development of a strategic direction, the establishment of a competency hub and the integration of unmanned systems into existing information systems. It also calls for investments in training, education and public trust-building initiatives.
The report is available for download on the Europol website and includes detailed insights, case studies and recommendations for law enforcement agencies, policymakers and other stakeholders.

CISA Unveils Enhanced Cross-Sector Cybersecurity Performance Goals

New Benchmarks Empower Organizations to Counter Emerging Threats, Build Cyber Resilience, and Strengthen Governance
the Cybersecurity and Infrastructure Security Agency (CISA) released version 2.0 of its Cross-Sector Cybersecurity Performance Goals (CPGs), offering organizations a more robust framework for integrating cybersecurity into daily operations. The updated CPGs align with the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) 2.0, incorporates three years of operational insights, and address emerging threats through data-driven, actionable guidance. These enhancements are designed to promote accountability, improve risk management, and support strategic cybersecurity governance across sectors.
The Cross-Sector CPGs represent a targeted subset of best practices, carefully selected through extensive consultation with industry leaders, government stakeholders, and cybersecurity experts. Designed to meaningfully reduce risks to critical infrastructure and safeguard the American public, these goals offer a practical starting point for small and medium-sized organizations. By focusing on a limited set of high-impact actions, the CPGs help prioritize cybersecurity investments that deliver measurable improvements in resilience and risk reduction.
The updated goals offer expanded and clarified guidance across key cybersecurity domains—including account and device security, data protection, governance, vulnerability management, supply chain risk, and incident response and recovery. Building on the foundation of version 1.0.1, CPG 2.0 introduces several notable improvements:
- Governance Emphasis: A new “Govern” function underscores the critical role of organizational leadership in cybersecurity, regrouping existing goals and introducing two new ones focused on risk management strategy, policy development, and executive accountability.
- Unified Goal Structure: Operational Technology (OT) and Information Technology (IT) goals are now consolidated into universal goals, eliminating silos across IT, Internet of Things (IoT), and OT environments.
- Threat-Responsive Expansion: New goals address emerging threats, third-party risk, zero trust architecture, and incident communication protocols.
- Streamlined Framework: Redundant, unclear, or underutilized goals have been removed to improve clarity and usability.
- Enhanced Documentation: Each goal now includes clearer methodology and supporting materials to reduce guesswork and improve implementation.
“Over the past year, CISA has engaged extensively with hundreds of stakeholders across both the public and private sectors to ensure the updated goals reflect real-world challenges and operational realities,” said Madhu Gottumukkala, Acting CISA Director. “Version 2.0 demonstrates our commitment to listening to and incorporating partner feedback to deliver practical, outcome-driven guidance that organizations can act on. These goals are applicable across all critical infrastructure sectors and offer foundational protection for organizations regardless of their cybersecurity maturity. We encourage all organizations to adopt the new CPGs and continue sharing feedback to help us refine future iterations.”
The Cross-Sector CPGs serve three primary purposes:
- Provide measurable actions that critical infrastructure entities can take to achieve a basic level of cybersecurity.
- Bridge communication gaps between IT/OT technical staff and organizational leadership to align on cybersecurity priorities.
- Support strategic planning by offering clear guidance that informs both near- and long-term cybersecurity investments.
CISA encourages organizations to adopt the voluntary Cross-Sector CPGs. To learn more about the updated Cybersecurity Performance Goals and how they can support your organization’s cybersecurity program, visit Cross-Sector Cybersecurity Performance Goals and Objectives.

CISA Releases Dynamic New Guide for Stadium and Arena Owners to Fortify Operations, Mitigate Vulnerabilities and Elevate Emergency Preparedness

The Cybersecurity and Infrastructure Security Agency (CISA) released the Venue Guide for Mitigating Dependency Disruptions, a new resource designed to strengthen the resilience of public gathering venues. This guide provides stadium and arena owners and operators with baseline strategies to mitigate the consequences of potential disruptions to four critical lifeline sectors—including Energy, Water and Wastewater Systems, Communications, and Transportation.
CISA developed this guide in close collaboration with government and industry experts from the four lifeline sectors as a concise, actionable resource for stadium and arena owners. Tailored for major public gathering events- such as FIFA World Cup 2026, America 250, and 2028 Summer Olympics, the guide draws on lessons learned from recent disruptions at high-profile public gathering sports and entertainment facilities across the United States and internationally. It equips critical infrastructure stakeholders with a clear understanding of threats to lifeline sectors and provides effective strategies to safeguard operations, reduce vulnerabilities, and enhance preparedness.
“Today’s risk environment is rapidly evolving, posing serious threats and disruptions to U.S. critical infrastructure and public gathering venues,” said CISA Acting Director Madhu Gottumukkala. “CISA is committed to working hand-in-hand with our government and industry partners to deliver actionable guidance that helps mitigate these risks. This guide empowers venue owners and operators to proactively assess vulnerabilities tied to dependent lifeline services and integrate those insights into contingency planning—ultimately reducing potential consequences and strengthening operational resilience.”
The Venue Guide for Mitigating Dependency Disruptions aligns with Executive Order 14234 Establishing the White House Task Force on the World Cup 2026, Executive Order 14239 Achieving Efficiency through State and Local Preparedness, and Executive Order 14328 Establishing the White House Task Force on the 2028 Summer Olympics. This guide assists critical infrastructure and public venue owners and operations with:
- Understanding the lifeline sector dependencies and interdependencies that their venues may rely on;
- Assessing security risks and associated key components of a facility evaluation; and
- Focusing on continued information-sharing and relationship-building with key partners such as local services providers, first responders, and CISA Security Advisors.
“Robust partnerships are essential to safeguarding critical infrastructure and public gatherings. By sharing threat intelligence, risk mitigation strategies, and other vital information, we strengthen our collective ability to anticipate and respond to potential disruptions. CISA’s newly released guide empowers venue owners and operators to assess dependencies and implement targeted mitigation strategies,” said CISA Executive Assistant Director for Infrastructure Security Steve Casapulla. “We deeply value the insights and collaboration from our government and industry partners across four lifeline sectors, which were instrumental in shaping this timely and practical resource. CISA urges all organizations that host events to review the guide and take proactive steps to enhance infrastructure security and resilience.”

Mistaking AI vulnerability could lead to large-scale breaches, NCSC warns

NCSC raises alert on “dangerous” misunderstanding of emergent class of vulnerability in generative artificial intelligence (AI) applications.
The National Cyber Security Centre (NCSC) – a part of GCHQ – has shared critical insights cautioning cyber security professionals against comparing prompt injection and more classical application vulnerabilities classed as SQL injection.
A new blog advises that, contrary to first impressions, prompt injection attacks against generative artificial intelligence applications may never be totally mitigated in the way SQL injection attacks can be.
Unlike SQL mitigation techniques, which hinge on enforcing a clear separation between data and instructions, prompt injection exploits the inability of large language models (LLMs) to distinguish between the two.
Without action addressing this misconception, the NCSC warns, websites risk falling victim to data breaches exceeding those seen from SQL injection attacks in the 2010s, impacting UK businesses and citizens into the next decade.
Backing proactive adoption of cyber risk management standards, the NCSC challenges claims that prompt injections can be ‘stopped’.
Instead, it suggests efforts should turn to reducing the risk and impact of prompt injection and driving up resilience across AI supply chains.
As AI technologies become embedded in more UK business operations, the NCSC calls on AI system designers, builders and operators to take control of manageable variables, acknowledging that LLM systems are “inherently confusable” and their risks managed in different ways.

Disaster Assistance High-Risk Series: State and Local Response Capabilities

GAO was asked to review long-standing challenges and emerging issues in federal response efforts for recent disasters, including Hurricanes Helene and Milton, the 2025 Los Angeles wildfires, and the July 2025 Texas floods. In September 2025, GAO issued the first report in a series on disaster response, focusing on the federal response workforce. This second report in the series provides information on federal disaster preparedness and response assistance provided before and during recent disasters, variation in state and local response capabilities, and considerations for potential changes to disaster response roles.
Preparing for and responding to disasters, like hurricanes and wildfires, begins with state and local governments. But, their ability to do so varies widely. The federal government provides extensive support through grants, training, and other assistance.
In light of recent interest in reviewing the federal role in disaster response, federal and state officials told us what they would want policymakers to consider with any potential changes. This includes clear communication, time to prepare, and FEMA's federal coordination role.
This is the second report in a series on disaster response. The first was on the federal response workforce.
State Response Team Assisting after Hurricane Helene
All levels of government have a role in preparing for and responding to disasters, with the Federal Emergency Management Agency (FEMA) leading the federal response. It has been nearly 20 years since the Post-Katrina Emergency Management Reform Act of 2006 required actions—such as the development of a national preparedness system—to address shortcomings in the nation’s disaster response system. Federal, state, and local governments, however, continue to face challenges preparing for and responding to large-scale disasters. Recent disasters, such as Hurricanes Helene and Milton in 2024, the Los Angeles wildfires in early 2025, and the July 2025 flooding in Texas, demonstrate the need for government-wide action to deliver assistance effectively.
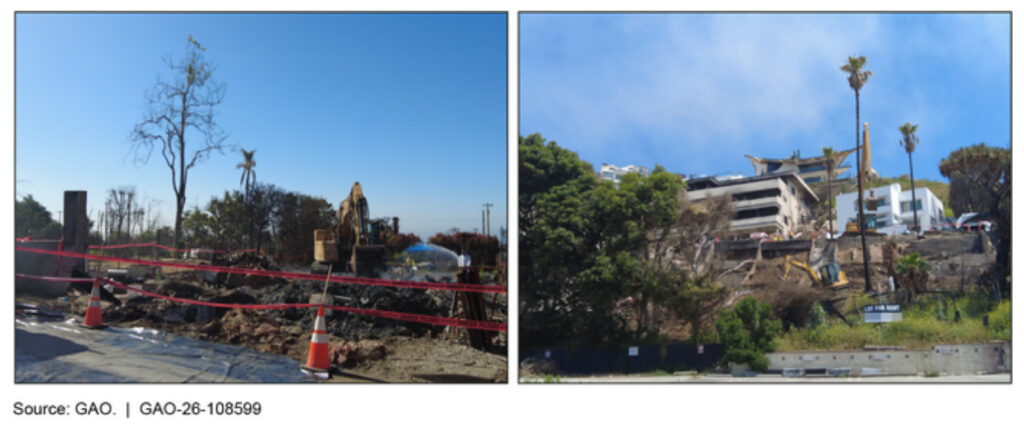
The federal government provides extensive support to state and local governments for disaster preparedness and response. For example, FEMA provides preparedness grants, training, and technical support to strengthen state and local emergency management capabilities. FEMA and other federal agencies, such as the U.S. Army Corps of Engineers and the Environmental Protection Agency, also supplement state and local efforts during disaster response (see figure).
U.S. Army Corps of Engineers Debris Removal Efforts After 2025 Los Angeles Wildfires
GAO analyzed selected states’ assessments of their disaster response capabilities and found that capability levels varied widely. Federal, state, and local officials GAO interviewed also emphasized the variation in capabilities at the state and local level—including challenges for rural or less resourced jurisdictions, even if they are within a well-resourced state.
GAO has previously reported on challenges with FEMA and other federal agencies’ disaster assistance and added Improving the Delivery of Disaster Assistance to GAO’s High-Risk list in February 2025 to highlight the recommendations GAO has made to improve federal disaster efforts.
Congress and the President have signaled an interest in reforms to FEMA. For example, the President signed Executive Orders in January and March 2025, respectively, establishing a FEMA Review Council to recommend improvements to FEMA and requiring review and revision of response and preparedness policies. Broader reform of FEMA’s mission, structure, or operations may address long-standing challenges with federal disaster efforts. Given the current levels of federal support and wide variation in state and local response capabilities, officials at the federal and state levels provided the following considerations for policymakers for communicating and implementing any such changes:
- Clear communication and guidance. States raised concerns about the uncertainty of the future of FEMA’s role. For example, state officials said it is challenging to plan in the absence of clear, consistent, and accurate guidance and emphasized the importance of consistent messaging about any changes, including technical assistance and training. GAO’s work following Hurricane Katrina also emphasized the importance of communicating clear roles and responsibilities.
- Time to prepare. Given that state and local governments rely on significant federal disaster support, federal and state officials emphasized the need for adequate time for these entities to prepare for any changes in disaster response roles.
- Catastrophic or widespread disasters. Federal officials underscored that there will always be catastrophic disasters for which even the most well-equipped states would require some level of federal financial or other support.
- Federal-level coordination. FEMA also plays a vital role as the coordinating agency for the federal response to disasters. For example, FEMA has the statutory authority to assign other federal agencies to perform disaster response tasks that those agencies might not otherwise have authority to perform.
GAO analyzed information from interviews conducted with federal agencies involved in disaster response and state and local governments impacted by disasters in recent years. Additionally, GAO analyzed preparedness assessments for the 10 states that received major disaster declarations for these recent disasters. To provide information on preparedness and response assistance, we summarized data on FEMA’s obligations for these disasters and amounts awarded through selected FEMA preparedness grants.

Terrorist Watchlist: FBI Should Improve Outreach Efforts to Nonfederal Users

The Threat Screening Center, administered by FBI, is responsible for managing the terrorist watchlist. In recent years, Members of Congress have raised questions about how nonfederal entities use the terrorist watchlist.
GAO was asked to examine the use of the terrorist watchlist by nonfederal law enforcement entities. This report examines (1) nonfederal entities’ reporting of terrorist watchlist encounters to FBI and opportunities for improvement and (2) steps FBI has taken to ensure nonfederal entities’ awareness of watchlist policies through outreach and state-led trainings.
When state and local law enforcement officers encounter people—e.g., in traffic stops—officers check their names against state database systems. The systems will return an alert if a name potentially matches one on the terrorist watchlist, which is managed by the FBI.
In half the interviews with law enforcement agencies, officials said their officers may not always know how to properly respond to these alerts.
We recommended that the FBI develop a communications plan to tell law enforcement agencies about the policies around the terrorist watchlist, and a process to review states' training on the policies.
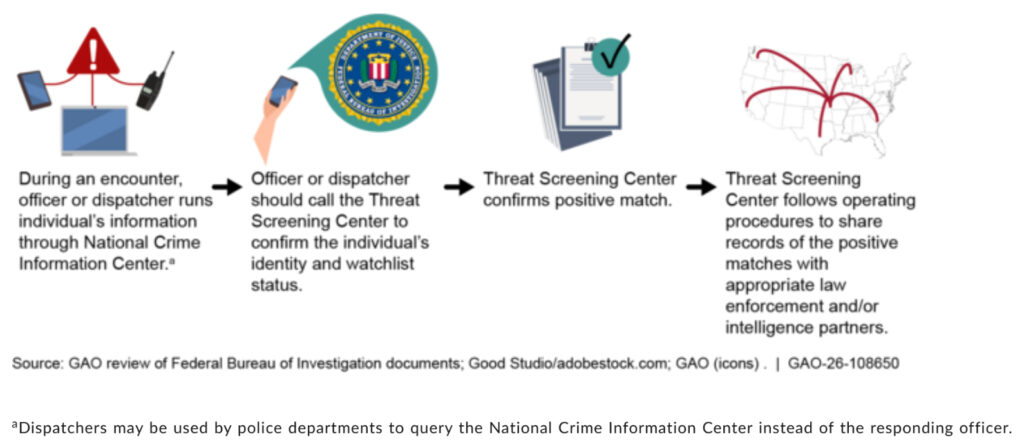
Nonfederal law enforcement officers query encountered individuals against the terrorist watchlist during routine police interactions, such as traffic stops. After encountering a potentially terrorist watchlisted individual, nonfederal law enforcement officers receive instructions, via the National Crime Information Center (NCIC), to contact the Federal Bureau of Investigation’s (FBI) Threat Screening Center to determine whether the individual is a positive or negative match to the terrorist watchlist.
GAO found that almost half of the law enforcement entities GAO interviewed in four states (12 of 26 entities, including police and sheriff’s departments) reported that officers were not consistently reporting encounters with potentially terrorist watchlisted individuals in instances where it is warranted. Seeking information to understand the extent to which nonfederal law enforcement entities are consistently reporting terrorist watchlist encounters could improve the accuracy of watchlist records.
Nonfederal Law Enforcement Steps When Responding To Terrorist Watchlist Encounters
The Threat Screening Center uses outreach efforts to communicate terrorist watchlisting policies to nonfederal law enforcement entities that use the terrorist watchlist. However, GAO found that FBI has not ensured nonfederal law enforcement entities are aware of terrorist watchlist policies and has not taken steps to develop a communication plan for its outreach efforts. Developing a communication plan with goals and measures as well as periodic assessments of progress would help accomplish this. Additionally, FBI’s Criminal Justice Information Services does not ensure states train NCIC users on terrorist watchlist policies. Without developing a process to review states’ efforts to do so, FBI cannot ensure that state training programs instruct nonfederal law enforcement to properly protect and respond to terrorist watchlist information.
GAO reviewed watchlist policies and training resources for nonfederal entities and collected encounter data for fiscal years 2019 through 2024. GAO interviewed nonfederal law enforcement officials in four states selected based on the number of encounters and other factors. While not generalizable, these interviews provided insights into officials’ awareness of policies and training.
This is the public version of a sensitive report GAO issued in August 2025. Information on encounter data and official FBI instructions on handling watchlist encounters that FBI deemed sensitive has been omitted.
GAO recommends that FBI (1) seek information to understand the extent to which nonfederal law enforcement entities are consistently reporting terrorist watchlist encounters, (2) develop a communication plan to improve its outreach efforts, and (3) develop a process to review state efforts to instruct NCIC users about watchlist policies. FBI concurred with the recommendations.

CISA Launches New Platform to Strengthen Industry Engagement and Collaboration

The Cybersecurity and Infrastructure Security Agency (CISA) launched a new Industry Engagement Platform (IEP) designed to facilitate structured, two-way communication between the agency and companies developing innovative and security technologies. The IEP enables CISA to better understand emerging solutions across the technology ecosystem while giving industry a clear, transparent pathway to engage with the agency.
“With the launch of this new platform, we’re opening the door wider to innovation—giving industry a direct line to share the tools and technologies that can help CISA stay ahead of evolving threats,” said CISA Acting Director Madhu Gottumukkala. “The private sector drives innovation and this collaboration is essential to our national resilience.”
The IEP allows organizations – including industry, non-profits, academia, government partners at all and the research community – with a structured process to request conversations with CISA subject matter experts to describe new technologies and capabilities. These engagements give innovators the opportunity to present solutions that may strengthen our nation’s cyber and infrastructure security.
Through customizable technology profiles, the IEP helps connect organizations to the right CISA experts by capturing areas of expertise and specific topics organizations wish to discuss. Participants may also upload capability overviews for CISA to reference in market research and in understanding emerging technologies across sectors.
While participation in the IEP does not provide preferential consideration for future federal contracts, it serves as a key channel for CISA to gain insight into new capabilities and market trends that support mission needs.
CISA encourages organizations with new, emerging, or advanced technology solutions to visit the Industry Engagement Platform. Current areas of interest include:
- Information technology and security controls
- Data, analytics, storage, and data management
- Communications technologies
- Any emerging technologies that advance CISA’s mission, including post-quantum cryptography and other next-generation capabilities
“Strategic collaboration is essential to strengthening national security and resilience,” Gottumukkala added. “The IEP is one of the ways CISA is aligning innovation with mission needs to advance the defense of our nation’s cyber and critical infrastructure.”

Key international organizations align on AI standards

International standardization bodies have pledged to cooperate on standards for artificial intelligence (AI), aiming to help build an open, sustainable and secure future for all.
The International Electrotechnical Commission (IEC), the International Organization for Standardization (ISO), and the International Telecommunication Union (ITU), at their latest global meeting in Seoul, Republic of Korea, issued a joint commitment to advance the well-being of humanity through AI standards.
The International Summit on AI Standards explores the complex challenges posed by AI and the opportunity to bridge digital divides through effective international standards.
The Seoul Statement enshrines a joint by the three organizations to advance AI standards for the benefit of everyone worldwide.
“Standards are technical tools to uphold the principles we want to live by,” said Seizo Onoe, Director of the Telecommunication Standardization Bureau at ITU. “The vision set out by this joint statement calls for diverse expertise and global commitment to collaboration and consensus – exactly what drives our standards work and exactly the spirit needed to create the future we want.”
A shared vision of AI for humanity
The statement sets out a joint vision and commitments from ITU, ISO and IEC on how technical standards can support the development and deployment of trustworthy AI systems that benefit society, drive innovation, and uphold fundamental rights.
“AI has the potential to bring profound benefits to people and economies across the globe,” said ISO President Sung Hwan Cho. “But to ensure this potential is realized equitably and responsibly, International Standards are essential. This joint statement reflects our commitment to strengthening cooperation across our organizations to deliver relevant, robust and human-centric standards that guide the responsible design and use of AI technologies.”
The summit brought together over 300 participants from 65 countries to share perspectives from government, industry, academia, civil society, the public and private sectors, international organizations and UN agencies.
Reliability and sustainability are crucial for standards to advance the global good. So is respect for human rights.
“The rapid rise of AI confirms a basic truth: technology is always about people,” said IEC President Jo Cops. “As AI becomes central to the global economy, we must urgently establish a guiding framework. This joint commitment underscores the value of international standards as the blueprint for safe, trustworthy, and people-centered AI development.”
Key commitments
The Seoul Statement outlines four key commitments to advance sustainable development and allow everyone to benefit from the AI revolution.
Together, IEC, ISO and ITU have pledged to:
- Actively incorporate socio-technical dimensions in standards development.
- Deepen the understanding of the interplay between international standards and human rights, recognizing both their importance and universality.
- Strengthen an inclusive, dynamic multistakeholder community to develop and apply international standards for the design, deployment, and governance of AI.
- Enhance public-private collaboration on AI capacity building.

Energy resilience in the Netherlands: application of the CER directive and identification of critical entities

The resilience of essential services is a cornerstone for national security and societal stability in the European Union. With this in mind, and as a response to emerging threats and interdependencies between critical infrastructure sectors, the EU introduced in 2022 the Critical Entities Resilience (CER) directive. One of the main points in this directive instructs member states to identify the critical entities that ensure the continuity of essential services across these sectors, including energy. This paper presents the collaboration efforts between the Netherlands Organization for Applied Scientific Research (TNO) and the Dutch Ministry for Climate and Green Growth (KGG) to apply the CER directive to the Dutch energy sector. The project aims to develop a reliable and repeatable method to determine the list of critical entities for each of the selected sectors: natural gas, oil, electricity and district heating.
The proposed method is based first on the definition of the value chains for each subsector followed by the development of a threshold framework that could be used to assess the criticality of processes and entities within the sector. Both pieces of work are then combined in a systematic way to arrive to the final lists of critical entities. The paper starts by presenting the value chains and how they were assembled in Section 2, followed by an explanation of the threshold framework in Section 3. The combination of both approaches and the full method and its application are then outlined in Section 4. The paper  concludes with the main findings and implications of this project in Section 5.
Energy sector value chains
In order to identify the critical entities of the energy sector in the Netherlands, a global overview of each subsector is needed. This overview allows the identification of the critical processes within each energy subsector and the interdependencies between them. This was built in the form of value chains for each subsector. A value chain is defined as the series of steps needed to convert raw energy carrier into a useful resource to consumers and deliver it to said consumers or commercial agents. For example, in the case of oil, this comprises the whole process from crude oil extraction to the delivery of oil products to users. Each value chain is divided into multiple sections that contain a series of processes, subprocesses and assets. A process is defined as each of the activities that enables the previously established value chain. The type of processes can range from engineering, such as production or treatment of an energy carrier, to logistical like transmission and distribution, or commercial, like energy trading, among other types. Each of these processes is carried out by one or multiple entities. An asset is defined as a piece of infrastructure or equipment that enables the previously defined processes. These assets are usually owned and maintained by the entity responsible for said process. The general structure used to build these value chains is shown in Figure 1.
As seen in the figure, these chains provide a clear overview of the main processes involved in each subsector, the main entities responsible for each process and subprocess, and finally, the interrelation and interdependencies between processes. One of the early challenges when defining these values chains is defining their scope. Since the CER directive focuses on entities that enable the value chain in each member state, the limits of the value chain were placed on the processes that happen within the Netherlands. At the edge of these value chains, are the interfaces with neighbouring countries, usually in the form of border connections. The CER directive focuses on the entities that enable the value chain, so final consumers are excluded from the analysis. To further illustrate this with an example, a portion of the oil value chain is shown in Figure 2. This diagram shows the first stages of the value chain, where the oil is produced from different sources or imported into the Dutch system. At each stage, each of the necessary processes is shown, such as onshore and offshore production or crude and oil products storage.
The identification of the processes for each sector was elaborated through a combination of sources. The main one was internal expertise across departments specialising on different energy carriers within TNO. At the same time, during the construction of these value chains, experts from the field, belonging to different entities responsible for each process, were consulted. Aside from this visual representation, a separate spreadsheet mirroring the diagram for each subsector was built. These spreadsheets contain more detailed information on the subsector, including energy volumes, detailed lists of assets and the full list of entities present at each process. The information used to build these overviews was extracted from public sources such as [1], [2] and [3]. This data allowed a better understanding of the weight of each process and subprocess, facilitating the later identification of the critical entities.
All of the processes discussed until now refer to the state of the sectors at the time of writing in 2025. An additional exercise was performed, where an outlook on the state of each subsector was analysed for 2035. In this case, instead of elaborating the whole value chain, only differences with 2025 were illustrated. Examples of this are the expected drop in production of natural gas in the Netherlands [4] or changes in the Dutch refinery market [5]. Additionally, hydrogen was included as a new sector that could play a more significant role in 2035.
Threshold framework
After defining the value chains for each subsector, a clear overview of all the processes and entities is now possible. In order to identify which of these processes are critical, a quantitative framework was established in order to identify the critical processes in a clear, repeatable and uniform way.
For each subsector studied, the CER directive [6] identifies a series of critical entity categories, shown in Table 1. In turn, each of these entities has a series of processes and entities that enable their services. In order to determine if an entity is critical according to the CER, this entity must be essential to enable said process. The question then comes down to what makes an entity essential in the context of a given service. This assessment can be done through a threshold framework. Each service can be assigned one or more thresholds based on a series of criteria. If an entity that provides such service exceeds one or more of these thresholds, it can be then considered critical. The CER directive defines a series of criteria to define these thresholds, shown in Table 2. As seen, all these criteria have a qualitative description and the challenge then becomes the quantification of these thresholds.
The first criterion refers to the number of users that are dependent on an entity that provides one of the services listed in Table 1. To establish a threshold for this parameter two different sources were used: the Dutch risk assessment guideline for integrated national security risk analysis [7] and the values already used by neighboring countries such as Germany, Belgium and Denmark. Each of the subsectors studied have different characteristics and scales they operated within, resulting in different threshold values for each subsector.
To asses interdependencies between CER sectors, first the dependencies between the energy subsectors needs to be determined. Firstly, all of the subsectors are directly dependent on the electricity subsector, powering a significant part of the processes that enable all of the value chains. In the case of natural gas, dependencies were identified in the electricity and heat subsectors, mostly related to natural gas powered boilers and energy stations. In the case of oil, some of the electricity processes, such as emergency diesel power generation were identified. Finally, in the case of heat, no other sector was identified as dependent on it. Furthermore, the CER directive identifies ten other critical sectors, such as transport, government services, wastewater or public health among others. Additionally, member states can add their own sectors to the list, with water management being an important one for the Netherlands. All of these critical sectors can be dependent on the studied energy subsectors. When trying to identify critical entities, it is also important to evaluate whether any of these critical sectors are dependent on them.
An entity can be considered critical if an incident that would affect it would cause a significant disruption to society. In this context, the magnitude of this impact depends on the duration and the severity of the incident. The main source used to assess the weight of a potential disruption duration was [7]. This national guideline defines the severity of an incident based on the duration of it and the number of users affected by it. In the case of electricity, gas and heat this threshold can also be addressed from the angle of security of supply. In the Netherlands, operators are obliged to compensate users economically depending on the duration of the outage. In the case of the oil sector,  a national emergency plan exists, born from the legacy of past oil supply crises [8], where different severity levels are activated based of established thresholds. At the same time, entities have been appointed to permanently maintain established strategic stock levels of crude oil and products at all times to mitigate the impact of potential disruptions.
In addition to the duration of the disruption, in [7] the impact on societal interests are also considered when evaluating the impact of a disruption. In the context of energy, special mention is made to critical off-takers. Regular households are usually covered by the ‘number of users’ criterion, but critical users, such as schools or hospitals, need to be evaluated separately. Entities that directly supply these users can be also considered critical, even if the total number of users does not meet the other thresholds. Additionally, possible severe impacts on the environment can also be considered as severe societal impact. Entities that, in case of failure, would cause environmental disasters, can also be considered critical.
The size and composition of the market that provides the critical service can also play a role in the critical entities determination. A market share threshold can be used to assess this. In the case of a market with a monopoly or oligopoly (either natural or regulated), entities responsible for it are directly critical. In the case of a competitive market, an appropriate value has to be defined as a threshold.
Regarding the threshold of geographic area, two aspects are of importance: the geographic cover of the entity and connections to neighboring countries. In the case of electricity and gas in the Netherlands, the sector is divided into geographic areas that are supplied by given network operators. In most of these cases, the areas contain enough households to reach the number of households threshold previously defined, making most of these operators critical. In the case of the heat networks, they tend to be more localized and cover a smaller number of users, requiring extra analysis when defining the critical operators. In the case of cross border-connections, the Netherlands acts as an energy hub for the electricity, natural gas and oil energy carriers.
The final criterion suggested in the CER is the importance of a given entity for the supply of a critical service. This is the most general criterion described in this section and can be used to appoint as critical entities that play a special role in the supply chain of an energy subsector. This usually concerns entities that, if disrupted, can cause major failures or fallouts in the rest of the value chain without reaching any of the previously defined thresholds.
Using all of the criteria and sources described in this section, a collection of thresholds for every CER service was compiled for each subsector. For the sake of illustration, an extract of this threshold collection is shown in Table 3 for the oil sector in the Netherlands. The exact threshold values have been redacted due to confidentiality reasons. An entity that provides at least one of the essential services and has a large enough presence to exceed the thresholds is considered critical. For this reason, exceeding a single threshold value is enough to appoint that entity critical, even in cases where the service has multiple critical thresholds. Additional tables like Table 3, one for each subsector, can then be used to identify the critical entities present within it.
Identification of critical entities
After describing the value chains for every subsector and compiling the full list of threshold values for every essential service, the final step was to apply all this to build the final list of critical entities. Before this took place, a first version of the value chains and the threshold framework was shared with prominent entities within the electricity, natural gas, oil and district heating subsectors in the Netherlands. The list of organizations to consult was assembled together between TNO and KGG, consisting of both private and public entities and regulators. After collecting all the feedback, a final version of the value chains descriptions and the threshold framework was elaborated. With this work in place, it was now possible to determine the critical entities for each sector. The method used to accomplish this is described in this section.
As explained in Section 2, each subsector was described using a series of processes and subprocesses, with each of them having a list of entities assigned to it. These processes are useful to describe the value chains from a physical point of view, identifying the fundamental steps and the relationship between them. The main limitation of this description is that it does not match one-to-one the essential services described in the CER. This can be overcome by mapping every subprocess in the value chain to its corresponding CER service. This can be done by applying specific sector knowledge to make the connections. An example result is conceptually shown in Figure 3, where it can be seen that an essential CER service can cover one or multiple processes from the value chains. At the same time, there are subprocesses that do not match any of the CER services.
As explained in Section 2, each process of the value chain was assigned the main entities that enable it at a national level.
Thanks to this, once every service has been mapped onto the value chain, it is now possible to link every entity to its corresponding CER service. Combining this insight, with the threshold framework information, it was now possible to link every entity to its corresponding threshold criteria. This is done by using tables such as Table 3, where each service (and now entity) can be assigned a series of threshold criteria and values.
The final step before being able to appoint the critical entities, is to score each entity according to the threshold criteria assigned to it. Again, using the corresponding table for each sector, such as Table 3, every threshold criterion has a parameter assigned to it. This can be for example, number of connections to other countries, total national market share, or specific energy volumes, among others. By researching each sector and entity, it is usually possible, by using publicly available data, to compute these values for each of the previously identified entities.
After completing all of the previous steps, every entity of the value chain is categorized in one of the CER essential services, its threshold criteria identified and how it scores according to this criteria. The final step is to compare the scores of each entity with the maximum threshold values for each criterion, defined in Section 3. If an entity has a single threshold score above the maximum allowed threshold criteria values, it is defined as a critical entity. Applying this process for each sector, service and entity, results in a list with the critical entities requested by the CER directive.
In summary, the method described is structured as follows:
1. Identify every process and subprocess that enable the value chain of the subsector and the relationships between them.
2. For each process and subprocess, identify and collect the main entities responsible for it.
3. Using the criteria defined in the CER, establish a list of threshold values for every critical service also defined in the CER.
4. Map every essential service to its corresponding processes and subprocesses from the value chains defined in step 1.
5. For every essential service, assign it all of the entities previously defined in step 2 that correspond to every (sub)process collected in step 4.
6. Based on the threshold framework developed in step 3, assign the corresponding threshold to every entity, depending on the essential service(s) it is assigned to.
7. Compute every entity’s threshold score for every criteria assigned to it in step 6.
8. Identify what entities have threshold values that exceed the threshold limits defined in step 3.
9. All of the entities that come out from step 7 are assembled into the final list of critical entities.
This method was developed by TNO with advice and support provided by KGG and entities and regulators of each subsector. Once the method was developed and all of the necessary data collected, it was then put into practice in a series of workshops. Each workshop was set to cover one subsector with the goal of reaching the final list with all of its corresponding entities. The parties present in these workshops were the corresponding sector expert groups from TNO, the group responsible for the critical entities appointment at KGG and some key experts from entities within the sectors. Aside from the final list of entities, these workshops also yielded some additional insights. One of them was that, while applying the threshold criteria to entities, in cases where there were multiple of them, one usually dominated. This reduced the number of criteria conflicts and could allow to streamline the threshold framework in a second iteration. Another important insight, is that the list of selected entities can vary significantly depending on the exact threshold values selected. In these cases, additional arguments, such as information from neighboring countries, can be useful to define a more robust threshold value. Finally, it was found that not all CER services are relevant to all countries. For example, only a selection of countries will have entities that will meet the minimum threshold values for fossil fuel production services.
Through this process, TNO provided the ministry with a robust, repeatable method. This method can be applied to any of the discussed energy subsectors and used as a blueprint to identify the critical entities within them. However, the ministry is the responsible body that will ultimately decide which entities will be appointed as critical. As previously mentioned, this method was applied to the current energy landscape in the Netherlands. As future work, it would be interesting to apply this method to different time and geographical scales. The energy sector is expected to change significantly in the coming decades, with new players emerging and old ones fading out. Applying the presented method to the expected sector in ten or twenty years from now could provide useful insights into the evolution of the sector. At the same time, applying it to a European scale could highlight important international dependencies within the continent. Finally, this method does not have to be necessarily limited to the energy sector. It could potentially be applied to other critical sectors that operate in a similar way through value chains and commodity deliveries. Examples of possible sectors could be drinking water management or food production. Finally the current analysis has been performed at a fairly high and abstract level. There could be potential value to be added by including a more quantifiable approach. This could be done through energy network modeling and specific risk scenario analysis.
Conclusion
Through this paper, a methodology was presented and applied for the determination of the Dutch critical entities of the energy subsectors, defined in the EU CER directive. By defining the value chains for each subsector, (natural gas, oil, electricity and district heating), a comprehensive understanding of the main processes and entities present in each of them was established.
After this, a threshold framework was developed to evaluate the criticality of each of these processes and entities. This framework was grounded in the criteria defined also in the CER, including sector dependencies, societal impact and geographic and market shares, among others. The threshold values and categories were tailored for each subsector and service by applying public sources, expert knowledge and consultations to important sector entities.
These two pieces of work were then combined to establish the method applied to appoint the final lists of critical entities. This was done by mapping the processes and entities identified in the value chains to the services and threshold criteria established in the threshold framework. Then, during workshops held between TNO experts, KGG and sector representatives, every entity was classified into its corresponding CER service and their position respect to the established threshold values computed. The application of this method can be used to compile a final list of critical entities for each subsector.
The outcome of this method enables a systematic and robust approach for the determination of the critical entities as defined in the CER directive. This work contributes to a more resilient energy system in the Netherlands, rooted in a repeatable and fact based approach built in collaboration with the subsectors themselves. It also sets the pillars for future updates and refinements and enables the Netherlands to adapt to a changing energy and threat landscape in the coming decades.
By J. Santiago Patterson, J. van Diemen, M.J.J. Scheepers, TNO
1 3 4 5 6 7 70