DOD Cybersecurity: Enhanced Attention Needed to Ensure Cyber Incidents Are Appropriately Reported and Shared
DOD and DIB information technology systems continue to be susceptible to cyber incidents as cybersecurity threats have evolved and become more sophisticated. Federal laws and DOD guidance emphasize the importance of properly reporting and sharing cyber incident information, as both are vital to identifying system weaknesses and improving the security of the systems.

House Report 116-442 included a provision for GAO to review DOD's cyber incident management. This report examines the extent to which DOD established and implemented a process to (1) report and notify leadership of cyber incidents, (2) report and share information about cyber incidents affecting the DIB, and (3) notify affected individuals of a PII breach.

To conduct this work, GAO reviewed relevant guidance, analyzed samples of cyber incident artifacts and cyber incident reports submitted by the DIB and privacy data breaches reported by DOD, and surveyed 24 DOD cyber security service providers. In addition, GAO interviewed officials from DOD and cyber security service providers and convened two discussion groups with DIB companies.

Cyber attacks threaten national security—but hackers continue to target DOD as well as private companies and others involved in the nation's military operations.

DOD has taken steps to combat these attacks and has reduced the number of cyber incidents in recent years. But we found that DOD:
- Hasn't fully implemented its processes for managing cyber incidents
- Doesn't have complete data on cyber incidents that staff report
- Doesn't document whether it notifies individuals whose personal data is compromised in a cyber incident

What GAO Found

The Department of Defense (DOD) and our nation's defense industrial base (DIB)—which includes entities outside the federal government that provide goods or services critical to meeting U.S. military requirements—are dependent on information systems to carry out their operations. These systems continue to be the target of cyber attacks, as DOD has experienced over 12,000 cyber incidents since 2015 (see figure).To combat these incidents, DOD has established two processes for managing cyber incidents—one for all incidents and one for critical incidents. However, DOD has not fully implemented either of these processes.

Despite the reduction in the number of incidents due to DOD efforts, weaknesses in reporting these incidents remain. For example, DOD's system for reporting all incidents often contained incomplete information and DOD could not always demonstrate that they had notified appropriate leadership of relevant critical incidents. The weaknesses in the implementation of the two processes are due to DOD not assigning an organization responsible for ensuring proper incident reporting and compliance with guidance, among other reasons. Until DOD assigns such responsibility, DOD does not have assurance that its leadership has an accurate picture of the department's cybersecurity posture.

In addition, DOD has not yet decided whether DIB cyber incidents detected by cybersecurity service providers should be shared with all relevant stakeholders, according to officials. DOD guidance states that to protect the interests of national security, cyber incidents must be coordinated among and across DOD organizations and outside sources, such as DIB partners. Until DOD examines whether this information should be shared with all relevant parties, there could be lost opportunities to identify system threats and improve system weaknesses.

DOD has established a process for determining whether to notify individuals of a breach of their personally identifiable information (PII). This process includes conducting a risk assessment that considers three factors—the nature and sensitivity of the PII, likelihood of access to and use of the PII, and the type of the breach. However, DOD has not consistently documented the notifications of affected individuals, because officials said notifications are often made verbally or by email and no record is retained. Without documenting the notification, DOD cannot verify that people were informed about the breach.

GAO is making six recommendations, including that DOD assign responsibility for ensuring proper incident reporting, improve the sharing of DIB-related cyber incident information, and document when affected individuals are notified of a PII breach. DOD concurred with the recommendations.
CISA Developed Cross-Sector Recommendations to Help Organizations Prioritize Cybersecurity Investments

The Department of Homeland Security released the Cybersecurity Performance Goals (CPGs), voluntary practices that outline the highest-priority baseline measures businesses and critical infrastructure owners of all sizes can take to protect themselves against cyber threats. The CPGs were developed by DHS, through the Cybersecurity and Infrastructure Security Agency (CISA), at the direction of the White House. Over the past year, CISA worked with hundreds of public and private sector partners and analyzed years of data to identify the key challenges that leave our nation at unacceptable risk. By clearly outlining measurable goals based on easily understandable criteria such as cost, complexity, and impact, the CPGs were designed to be applicable to organizations of all sizes. This effort is part of the Biden-Harris Administration’s ongoing work to ensure the security of the critical infrastructure and reduce our escalating national cyber risk.

“Organizations across the country increasingly understand that cybersecurity risk is not only a fundamental business challenge but also presents a threat to our national security and economic prosperity,” said Secretary of Homeland Security Alejandro N. Mayorkas. “The new Cybersecurity Performance Goals will help organizations decide how to leverage their cybersecurity investments with confidence that the measures they take will make a material impact on protecting their business and safeguarding our country.”

CISA developed the CPGs in close partnership with the National Institute for Standards and Technology (NIST). The resulting CPGs are intended to be implemented in concert with the NIST Cybersecurity Framework. Every organization should use the NIST Cybersecurity Framework to develop a rigorous, comprehensive cybersecurity program. The CPGs prescribe an abridged subset of actions – a kind of “QuickStart guide” – for the NIST CSF to help organizations prioritize their security investments.

“To reduce risk to the infrastructure and supply chains that Americans rely on every day, we must have a set of baseline cybersecurity goals that are consistent across all critical infrastructure sectors,” said CISA Director Jen Easterly. “CISA has created such a set of cybersecurity performance goals to address medium-to-high impact cybersecurity risks to our critical infrastructure. For months, we’ve been gathering input from our partners across the public and private sectors to put together a set of concrete actions that critical infrastructure owners can take to drive down risk to their systems, networks and data. We look forward to seeing these goals implemented over the coming years and to receiving additional feedback on how we can improve future versions to most effectively reduce cybersecurity risk to our country.”

“The Biden-Harris Administration has relentlessly focused on securing our Nation’s critical infrastructure since day one,” said Deputy National Security Advisor for Cyber and Emerging Technologies Anne Neuberger. “CISA has demonstrated tremendous leadership in strengthening our critical infrastructure’s cyber resilience over the last year. The Cyber Performance Goals build on these efforts, by setting a higher cybersecurity standard for sectors to meet.”

“Given the myriad serious cybersecurity risks our nation faces, NIST looks forward to continuing to work with industry and government organizations to help them achieve these performance goals,” said Under Secretary of Commerce for Standards and Technology and NIST Director Laurie E. Locascio. “Our priority remains bringing together the right stakeholders to further develop standards, guidelines and practices to help manage and reduce cybersecurity risk.”

In the months ahead, CISA will actively seek feedback on the CPGs from partners across the critical infrastructure community and has established a Discussions webpage to receive this input. CISA will also begin working directly with individual critical infrastructure sectors as it builds out sector-specific CPGs in the coming months.

To access these new CPGs visit CISA.gov/cpgs.

TSA issues new cybersecurity requirements for passenger and freight railroad carriers

The Transportation Security Administration (TSA) announced a new cybersecurity security directive regulating designated passenger and freight railroad carriers. Today’s announcement demonstrates the Biden-Harris Administration’s commitment to strengthen the cybersecurity of U.S. critical infrastructure. Building on the TSA’s work to strengthen defenses in other transportation modes, this security directive will further enhance cybersecurity preparedness and resilience for the nation’s railroad operations.

Developed with extensive input from industry stakeholders and federal partners, including the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA) and the Department of Transportation’s Federal Railroad Administration (FRA), this Enhancing Rail Cybersecurity – SD 1580/82-2022-01 strengthens cybersecurity requirements and focuses on performance-based measures to achieve critical cybersecurity outcomes.

“The nation’s railroads have a long track record of forward-looking efforts to secure their network against cyber threats and have worked hard over the past year to build additional resilience, and this directive, which is focused on performance-based measures, will further these efforts to protect critical transportation infrastructure from attack,” said TSA Administrator David Pekoske. “We are encouraged by the significant collaboration between TSA, FRA, CISA and the railroad industry in the development of this security directive.

The security directive requires that TSA-specified passenger and freight railroad carriers take action to prevent disruption and degradation to their infrastructure to achieve the following critical security outcomes:

1. Develop network segmentation policies and controls to ensure that the Operational Technology system can continue to safely operate in the event that an Information Technology system has been compromised and vice versa;
2. Create access control measures to secure and prevent unauthorized access to critical cyber systems;
3. Build continuous monitoring and detection policies and procedures to detect cybersecurity threats and correct anomalies that affect critical cyber system operations; and
4. Reduce the risk of exploitation of unpatched systems through the application of security patches and updates for operating systems, applications, drivers, and firmware on critical cyber systems in a timely manner using a risk-based methodology.

Passenger and freight railroad carriers are required to:

1. Establish and execute a TSA-approved Cybersecurity Implementation Plan that describes the specific cybersecurity measures the passenger and freight rail carriers are utilizing to achieve the security outcomes set forth in the security directive.
2. Establish a Cybersecurity Assessment Program to proactively test and regularly audit the effectiveness of cybersecurity measures and identify and resolve vulnerabilities within devices, networks, and systems.

This is the latest in TSA’s performance-based security directives; previous security directives include requirements such as reporting significant cybersecurity incidents to CISA, establishing a cybersecurity point of contact, developing and adopting a cybersecurity incident response plan, and completing a cybersecurity vulnerability assessment. Through this security directive, TSA continues to take steps to protect transportation infrastructure in the current threat environment. TSA also intends to begin a rulemaking process, which would establish regulatory requirements for the rail sector following a public comment period.

To view TSA’s security directives and guidance documents, please visit the TSA cybersecurity toolkit.

The importance of early warning systems in disaster risk reduction

It is not enough for an early warning system to correctly identify an incoming hazard, it must also ensure that the populations and sectors that are at risk can receive the alert, understand it, and most importantly, act on it.

Disasters, increasingly frequent and intense, have become a major issue requiring urgent action. In 2021, 432 catastrophic events took place, incrementing the average of 357 annual catastrophic events recorded in 2001-2020. Only last year, 101.8 million people were affected worldwide, and the economic losses amounted to 252.1 billion US dollars.

The impacts of a disaster are often unequally distributed, affecting disproportionately the most vulnerable. These events cause a disruption in the economy and livelihoods of people, producing dramatic socio-economic downturns that hamper short-term recovery and long-term development. On this basis, the promotion of resilience to face all kinds of shocks and stresses is considered a key element for the global development agenda.

In line with this perspective, and in accordance with its mandate, the International Labour Organisation (ILO) has focused on building resilience through the promotion of employment and decent work.

In order to achieve this, the ILO works with its tripartite constituents – governments and employers’ and workers’ organizations – to develop a response to disasters that can answer immediate needs, but also deploy a long-term vision to build resilience for risk management through employment-centred measures. These include skills development, job creation through employment-intensive investments, enterprise support and business continuity management, among others.

This year, the International Day for Disaster Risk Reduction focuses on early warning systems, a fundamental element to decrease the destructive impacts of a disaster. An effective early warning is capable of saving many lives and reducing damage by 30% if activated 24 hours before the event. However, today, one-third of the world’s population, mainly in the least developed countries, is still not covered by early warning systems.

The purpose of early warning systems is mitigating the risk produced by disasters, but these risks are compounded by the socio-economic vulnerability of the population exposed to the hazards. In this context, early warning systems must be inclusive and sensitive to the different sources of vulnerability. As indicated by the United Nations Office for Disaster Risk Reduction (UNDRR) , these systems must be people-centred, end-to-end, and multi-hazard.

Early warning systems play a significant role in the world of work. By disseminating timely and accurate information regarding disaster risk, they enable preparedness action as well as a rapid response from workers, employers, and national or local authorities, and can therefore prevent human and economic losses in the workplace. For instance, farmers, pastoralists, fishers, and foresters are among the most-at-risk communities to disasters. Moreover, early warning systems can also play a crucial role in decent work, as part of the occupational health and safety standards in disaster-prone countries.

Early warning systems are essential to prepare and respond effectively in the short term, corresponding to the first stages of disaster management. Moreover, the implementation of such systems can also contribute to building resilience, as enhancing preparedness strengthens the capacity to recover rapidly, and reduces vulnerability.

Forest fires: €170 million to reinforce rescEU fleet

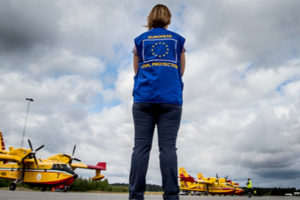
Following a record-breaking forest fire season in Europe, the Commission is proposing today €170 million from the EU budget to reinforce its rescEU ground and aerial assets  starting from the summer of 2023. The rescEU transitional fleet would therefore have a total of 22 planes, 4 helicopters as well as more pre-positioned ground teams. As from 2025, the fleet would be further reinforced through an accelerated procurement of airplanes and helicopters.

Commissioner for Crisis Management Janez Lenarčič said: "Due to climate change the number of regions affected by wildfires is increasing, going beyond the traditionally affected Mediterranean countries. The last summers have clearly shown that more firefighting assets are needed at EU-level. By building up our fleet of aerial means and ground forces, the EU will be able to ensure a prompt, flexible response, including in situations where fires are burning in multiple Member States at the same time.”

Commissioner for Budget and Administration, Johannes Hahn said: “While the record-breaking forest fires this summer may have been overshadowed by other crises, today's proposal to reinforce rescEU shows that the EU budget will continue to support those in need. European solidarity across EU Member States remains strong and we are ready to support this solidarity with financial means.”

Wildfires in the EU are increasing in scope, frequency, and intensity. By 1 October, the data for 2022 reveal a 30% increase in the burnt area over the previous worst year recorded (2017) and a more than 170% increase over the average burnt area since EU-level recording started in 2006.

This season, the Emergency Response Coordination Centre  received 11 requests for assistance for forest fires. 33 planes and 8 helicopters were deployed across Europe via the EU Civil Protection Mechanism, which were joined by over 350 firefighters on the ground. In addition, the EU's emergency Copernicus satellite provided damage assessment maps of the affected areas.

CISA Directs Federal Agencies to Improve Cybersecurity Asset Visibility and Vulnerability Detection

The Cybersecurity and Infrastructure Security Agency (CISA) issued a Binding Operational Directive (BOD) 23-01, Improving Asset Visibility and Vulnerability Detection on Federal Networks, that directs federal civilian agencies to better account for what resides on their networks.

Over the past several years, CISA has been working urgently to gain greater visibility into risks facing federal civilian networks, a gap made clear by the intrusion campaign targeting SolarWinds devices. The Biden-Harris Administration and Congress have supported significant progress by providing key authorities and resources. This Directive takes the next step by establishing baseline requirements for all Federal Civilian Executive Branch (FCEB) agencies to identify assets and vulnerabilities on their networks and provide data to CISA on defined intervals.

“Threat actors continue to target our nation’s critical infrastructure and government networks to exploit weaknesses within unknown, unprotected, or under-protected assets,” said CISA Director Jen Easterly. “Knowing what’s on your network is the first step for any organization to reduce risk. While this Directive applies to federal civilian agencies, we urge all organizations to adopt the guidance in this directive to gain a complete understanding of vulnerabilities that may exist on their networks. We all have a role to play in building a more cyber resilient nation.”

CISA is committed to using its cybersecurity authorities to gain greater visibility and drive timely risk reduction across federal civilian agencies. Implementation of this Directive will significantly increase visibility into assets and vulnerabilities across the federal government, in turn improving capabilities by both CISA and each agency to detect, prevent, and respond to cybersecurity incidents and better understand trends in cybersecurity risk.

This Directive is a mandate for federal civilian agencies. However, CISA recommends that private businesses and state, local, tribal and territorial (SLTT) governments review it and prioritize implementation of rigorous asset and vulnerability management programs.

The new Directive can be found at Binding Operational Directive (BOD) 23-01.

Public Health Emergencies: Data Management Challenges Impact National Response

Public health emergencies evolve quickly, but public health entities lack the ability to share new data and potentially life-saving information in real-time—undermining the nation's ability to respond quickly.

To address this, the federal government must overcome three major challenges—specifically, the lack of:

- Common standards for collecting data (e.g., patient characteristics)
- "Interoperability" (meaning not all data systems work together)
- Public health IT infrastructure (the hardware, software, networks, and policies that would enable the reporting and sharing of data)

This snapshot discusses our related work and recommendations.

Public health emergencies evolve quickly, but public health entities lack the ability to share new data and potentially life-saving information in near real-time. To address this, the federal government must overcome 3 major challenges in how it manages public health data. GAO has made a number of recommendations to help address these challenges. However, many of these recommendations have not been implemented.
The Big Picture

Longstanding challenges in the federal government’s management of public health data undermine the nation’s ability to quickly respond to public health emergencies like COVID-19 and monkeypox. These challenges include the lack of:

- common data standards—requirements for public health entitles to collect certain data elements, such as patient characteristics (e.g., name, sex, and race) and clinical information (e.g., diagnosis and test results) in a specific way;
- interoperability—the ability of data collection systems to exchange information with and process information from other systems; and
- public health IT infrastructure—the computer software, hardware, networks, and policies that enable public health entities to report and retrieve data and information.

Over 15 years ago, federal law mandated that the Department of Health and Human Services (HHS) establish a national public health situational awareness network with a standardized data format. This network was intended to provide secure, near real-time information to facilitate early detection of and rapid response to infectious diseases.

However, the federal government still lacks this needed network and has not yet overcome the challenges identified in previous GAO reviews. Having near real-time access to these data could significantly improve our nation’s preparedness for public health emergencies and potentially save lives.

Without the network, federal, state, and local health departments, hospitals, and laboratories are left without the ability to easily share health information in real-time to respond effectively to diseases.

GAO’s prior work identified three broad challenges to public health data management and recommended actions for improvement.

1. Common Data Standards

To ensure that information can be consistently reported, compared, and analyzed across jurisdictions, public health entities need a standardized data format. Due to the lack of common data standards, information reported by states about COVID-19 case counts was inconsistent. This in turn complicated the ability of the Centers for Disease Control and Prevention (CDC) to make comparisons. Public health representatives also noted challenges in collecting complete demographic data. This made it difficult to identify trends in COVID-19 vaccinations and the number of doses administered. Although CDC had intended to implement data standards, its strategic plan did not articulate specific actions, roles, responsibilities, and time frames for doing so.

- Re recommended that HHS establish an expert committee for data collection and reporting standards by engaging with stakeholders (e.g., health care professionals from public and private sectors). This committee should review and inform the alignment of ongoing data collection and reporting standards related to key health indicators.
- Recommended that CDC define specific action steps and time frames for its data modernization efforts.

2. Interoperability among Public Health IT Systems

The inability to easily exchange information across data collection and other data systems creates barriers to data sharing and additional burdens on entities that collect and transmit data. During the early stages of COVID-19, the lack of IT system interoperability caused health officials and their key stakeholders (e.g., hospitals) to manually input data into multiple systems. In addition, some state health departments could not directly exchange information with CDC via an IT system. This led to longer time frames for CDC to receive the data they needed to make decisions on the COVID-19 response.

- Recommended that, as part of planning for the public health situational awareness network, HHS should ensure the plan includes how standards for interoperability will be used.

3. Lack of a Public Health IT Infrastructure

The timeliness and completeness of information that is shared during public health emergencies can be impeded by the absence of a public health IT infrastructure. During the early stages of COVID-19, some states had to manually collect, process, and transfer data from one place to another. For example, a state official described having to fax documents, make copies, and physically transport relevant documents. The official noted by establishing a public health IT infrastructure, such as the network HHS was mandated to create, errors would be reduced. To help mitigate challenges in data management for COVID-19, HHS launched the HHS Protect platform in April 2020. However, we reported that public health and state organizations raised questions about the completeness and accuracy of some of the data.

- Recommended that HHS prioritize the development of the network by, in part, establishing specific near-term and long-term actions that can be completed to show progress.
- Recommended that HHS identify an office to oversee the development of the network.
- Recommended that HHS identify and document information-sharing challenges and lessons learned from the COVID-19 pandemic.

Makati City becomes the second Resilience Hub in Asia-Pacific

The City of Makati in the Philippines is named as the second Resilience Hub of Making Cities Resilient 2030 (MCR2030) in the Asia-Pacific region on 27 September 2022.

Makati has already been recognized as a Role Model City of the MCR 2010-2020 initiative by sharing know-how and experiences for reducing disaster risk, building urban resilience with other cities and participating in regional forums.

Under the leadership of Mayor Mar-len Abigail S. Binay, the city has adopted the principle of “Resilience is everybody’s business” at all sectors of society to manage disasters and build urban resilience in the country.

“We’re committed to continuing the journey of advocating resilience as a way of life through a Resilience Hub by collaborating with our constituents, partners and other local government units,” said Ms. Binay.

The Chief of the Regional Office for Asia and the Pacific at the United Nations Office for Disaster Risk Reduction (UNDRR), Mr. Marco Toscano-Rivalta, congratulated the Mayor, the City of Makati and its people for their vision and determination to continue strengthening disaster resilience and supporting other cities along the resilience pathway.

“Disaster risk is local, and it is at the local level where leadership, partnerships and solutions make a difference. MCR2030 is a catalyst for local action, a platform for collaboration and sharing of knowledge to localize disaster risk management and the implementation of the Sendai Framework for Disaster Risk Reduction,” said Mr. Toscano-Rivalta.

Makati, also known as a financial hub of the country, has developed a three-year plan of the Resilience Hub, which focuses on creating and building an online knowledge portal. The portal’s objective is to enhance peer-to-peer support, and disseminate risk data, information and expertise by conducting workshops, seminars and events related to strengthening urban resilience towards disaster risk reduction.

The plan also aims to improve city-to-city cooperation by working with other local governments in the Asia Pacific Region and beyond, promote synergies between cities to learn from each other and other disaster risk reduction activities, including capacity building, disaster preparedness, response and prevention.

The city is also in the process of developing the Makati Disaster Risk Reduction and Management Academy to learn from its best practices, using case studies and knowledge bases from other cities, leveraging experiences from an international group of practitioners who already participated in the initiative.

Notably, the city has continually mainstreamed and institutionalized disaster risk reduction management across all levels of the city since signing up to the MCR campaign in 2010.

As one of the pilot cities applying MCR tools, Makati held multi-sectoral annual workshops, reviewed and reassessed the city’s progress in implementing the Ten Essentials for MCR2030 through the Local Government Self-Assessment Tool.

The city was one of the first municipalities to utilize the Disaster Resilience Scorecard for Cities, which was developed through then UNISDR’s collaboration with global technology companies such as IBM and AECOM.

In 2017, the city established a resilience roadmap called the Makati Disaster Risk Reduction and Management Plan, using the now adapted Disaster Resilience Scorecard. Makati used Disaster Resilience Scorecard for Cities - Public Health System Resilience Addendum to enhance the city’s disaster risk reduction management.

UK and allies expose Iranian state agency for exploiting cyber vulnerabilities for ransomware operations

The UK and international allies have issued a joint cyber security advisory highlighting that cyber actors affiliated with Iran’s Islamic Revolutionary Guard Corps (IRGC) are exploiting vulnerabilities to launch ransomware operations against multiple sectors.

Iranian-state APT actors have been observed actively targeting known vulnerabilities on unprotected networks, including in critical national infrastructure (CNI) organisations.

The advisory, published by the National Cyber Security Centre (NCSC) − a part of GCHQ − alongside agencies from the US, Australia and Canada, sets out tactics and techniques used by the actors, as well as steps for organisations to take to mitigate the risk of compromise.

It updates an advisory issued in November 2021 which provided information about Iranian APT actors exploiting known Fortinet and Microsoft Exchange vulnerabilities.

They are now assessed to be affiliated to the IRGC and are continuing to exploit these vulnerabilities, as well as the Log4j vulnerabilities, to provide them with initial access, leading to further malicious activity including data extortion and disk encryption.

Paul Chichester, NCSC Director of Operations, said:

"This malicious activity by actors affiliated with Iran’s IRGC poses an ongoing threat and we are united with our international partners in calling it out.

“We urge UK organisations to take this threat seriously and follow the advisory’s recommendations to mitigate the risk of compromise.”

The NCSC urges organisations to follow the mitigation set out in the advisory, including:

- Keeping systems and software updated and prioritising remediating known exploited vulnerabilities
- Enforcing multi-factor authentication
- Making offline backups of your data

This advisory has been issued by the NCSC, the Federal Bureau of Investigation (FBI), the Cybersecurity and Infrastructure Security Agency (CISA), the National Security Agency (NSA), US Cyber Command (USCC), Department of the Treasury (DoT), the Australian Cyber Security Centre (ACSC) and the Canadian Centre for Cybersecurity (CCCS).

NSA, CISA: How Cyber Actors Compromise OT/ICS and How to Defend Against It

The National Security Agency (NSA) and the Cybersecurity and Infrastructure Security Agency (CISA) published a Cybersecurity Advisory that highlights the steps malicious actors have commonly followed to compromise operational technology (OT)/industrial control system (ICS) assets and provides recommendations on how to defend against them.

“Control System Defense: Know the Opponent” notes the increasing threats to OT and ICS assets that operate, control, and monitor day-to-day critical infrastructure and industrial processes. OT/ICS designs are publicly available, as are a wealth of tools to exploit IT and OT systems.

Cyber actors, including advanced persistent threat (APT) groups, have targeted OT/ICS systems in recent years to achieve political gains, economic advantages, and possibly to execute destructive effects. Recently, they’ve developed tools for scanning, compromising, and controlling targeted OT devices.

“Owners and operators of these systems need to fully understand the threats coming from state-sponsored actors and cybercriminals to best defend against them,” said Michael Dransfield, NSA Control Systems Defense Expert. “We’re exposing the malicious actors’ playbook so that we can harden our systems and prevent their next attempt.”

This joint Cybersecurity Advisory builds on previous NSA and CISA guidance to stop malicious ICS activity and reduce OT exposure. Noting that traditional approaches to securing OT/ICS do not adequately address threats to these systems, NSA and CISA examine the tactics, techniques, and procedures cyber actors employ so that owners and operators can prioritize hardening actions for OT/ICS.

Defenders should employ the mitigations listed in this advisory to limit unauthorized access, lock down tools and data flows, and deny malicious actors from achieving their desired effects.

1 … 19 20 21 22 23 … 48